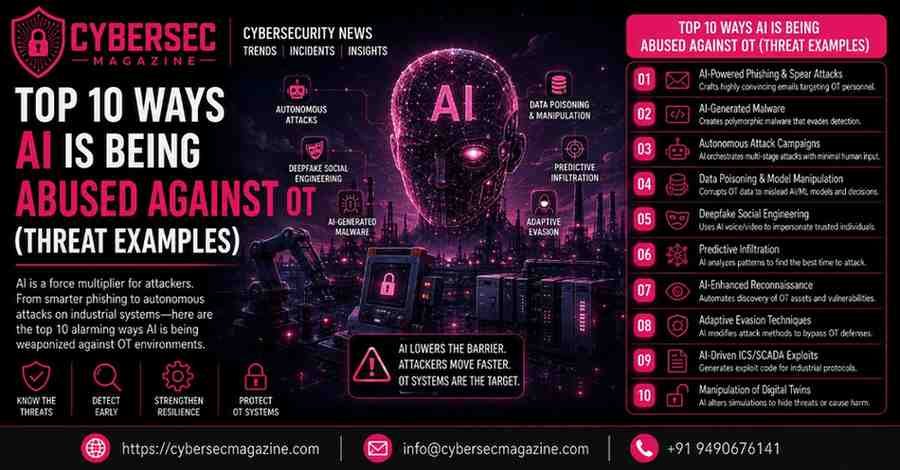
Welcome back to the cybersecurity desk. As an editor mapping the high-stakes convergence of IT, OT, and MIoT, I spend my days analyzing where sophisticated code meets physical infrastructure. Right now, a quiet revolution is rewriting the industrial threat landscape. We have spent years discussing how defenders can leverage machine learning for predictive maintenance and […]
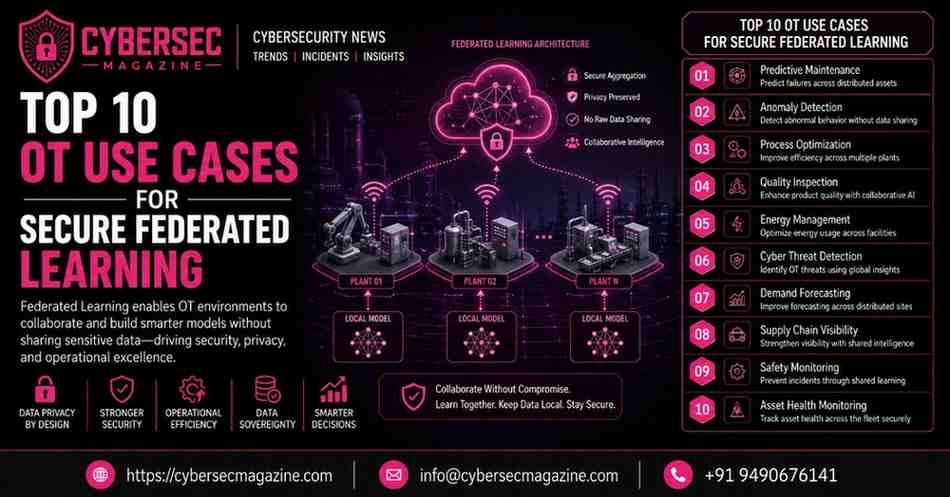
Top 10 OT Use Cases for Secure Federated Learning
In the high-stakes world of Operational Technology (OT), data is lifeblood-but it is also a massive liability. Traditionally, Industrial Control Systems (ICS) required centralizing sensitive telemetry to train security models, creating a single point of failure and massive privacy risks. Secure Federated Learning (FL) changes the paradigm by bringing the AI model to the data, […]
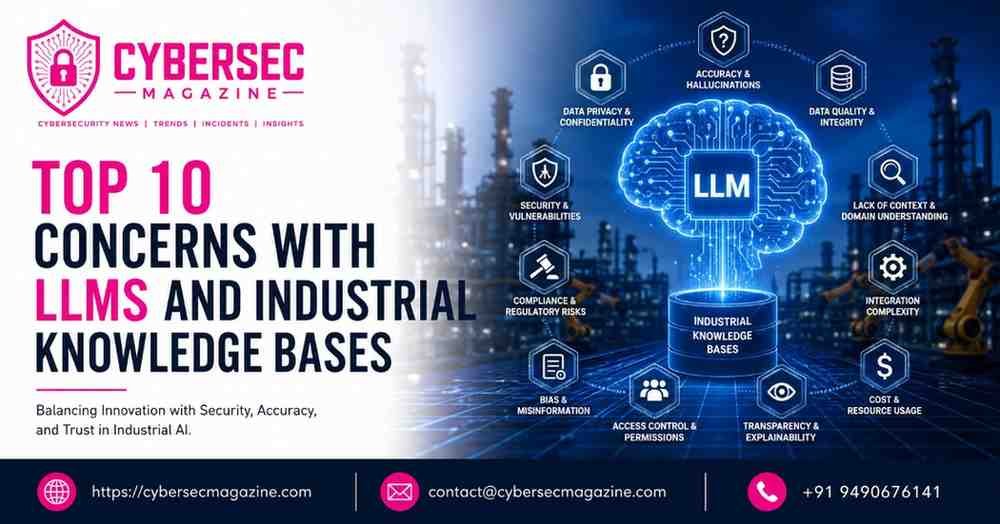
Top 10 Concerns with LLMs and Industrial Knowledge Bases
Welcome back to the cybersecurity desk. As an editor tracking the high-stakes convergence of IT, OT, and MIoT, I am watching a massive paradigm shift unfold on the factory floor. Every major industrial player is rushing to integrate Large Language Models (LLMs) into their operations. The pitch is undeniably attractive: ingest decades of proprietary maintenance […]
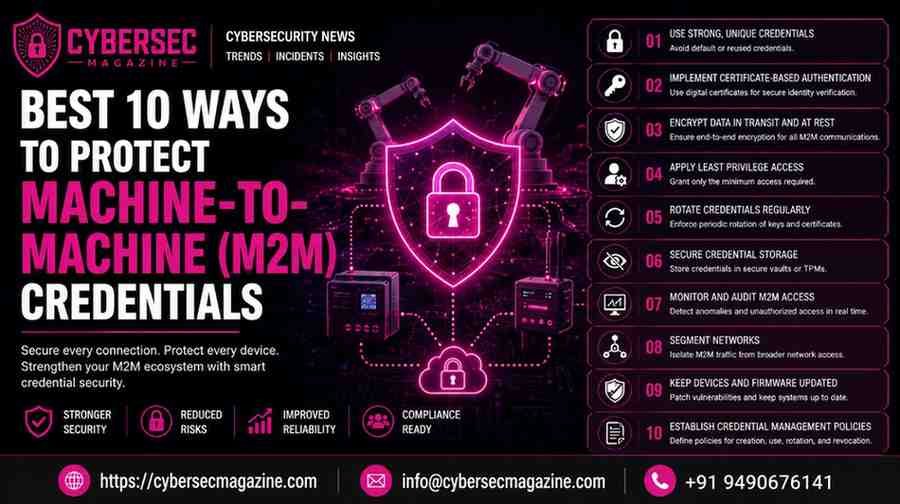
Best 10 Ways to Protect Machine-to-Machine (M2M) Credentials
Welcome back to the cybersecurity desk. As an editor mapping the high-stakes convergence of IT, OT, and MIoT, I spend a lot of time analyzing how humans authenticate. But in 2026, humans aren’t the primary users on our networks-machines are. As we scale microservices, deploy millions of Industrial IoT (IIoT) sensors, and connect legacy PLCs […]
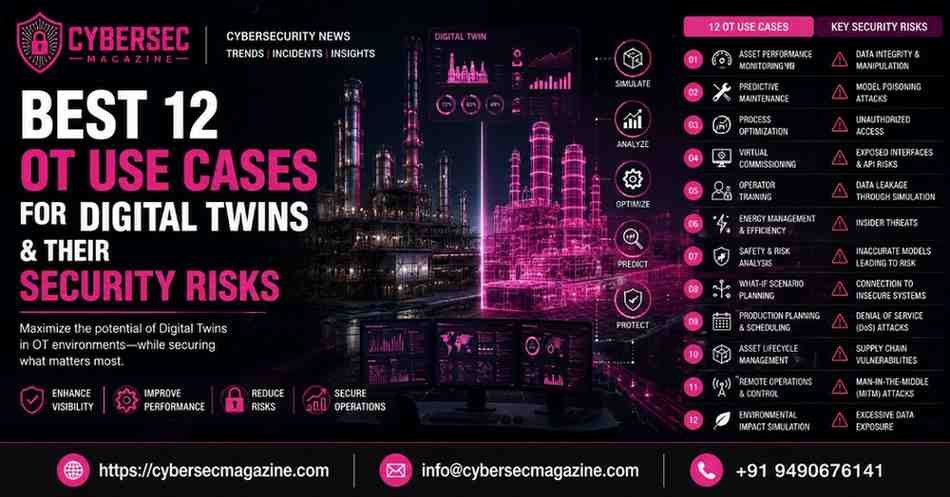
Top 12 OT Use Cases for Digital Twins & Their Hidden Security Risks
As a senior cybersecurity editor covering the high-stakes convergence of IT, Operational Technology (OT), and MIoT, I am witnessing a monumental shift in how we defend critical infrastructure. The global digital twin market is exploding, projected to jump from $18.9 billion in 2025 to over $26.4 billion in 2026, driven by an urgent need for […]
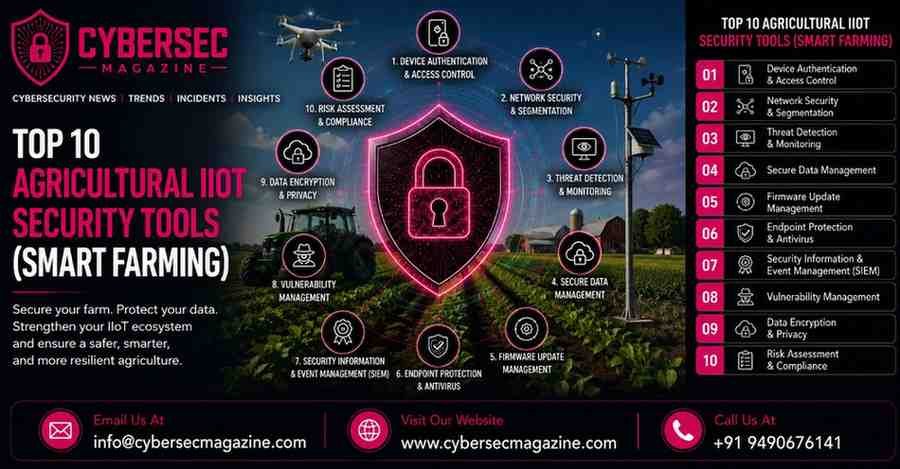
Securing the Harvest: Top 10 IIoT Security Tools for Smart Farming in 2026
Protect your agricultural infrastructure with the top 10 IIoT security tools. Enhance smart farming resilience and data integrity in the 2026 threat landscape. The Digital Fields of 2026: Why Security is the New Foundation Agriculture has transitioned from a labor-intensive industry to a data-driven powerhouse, where Industrial Internet of Things (IIoT) sensors, autonomous robotics, and […]
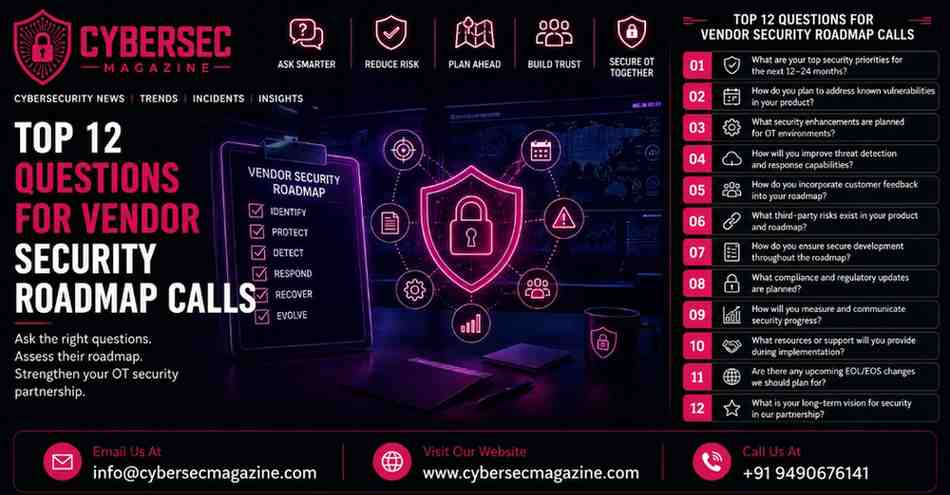
Top 12 Questions for Vendor Security Roadmap Calls (2026)
Master your vendor risk assessments in 2026. Discover the top 12 critical questions to ask for robust OT/ICS supply chain security and operational resilience. The New Reality of Industrial Procurement The days of treating cybersecurity as a secondary consideration during industrial procurement are over. In 2026, the convergence of IT and OT has turned every […]
Beyond Completion Rates: The Case for Behavioral Intelligence in Workforce Development
Early in my career, I found myself in a Pentagon conference room discussing a problem that put most workplace issues into perspective. The U.S. Army was losing roughly twenty-five soldiers per month to suicide. In that room, no one was concerned about whether an intervention would be completed or how many people would attend. The […]
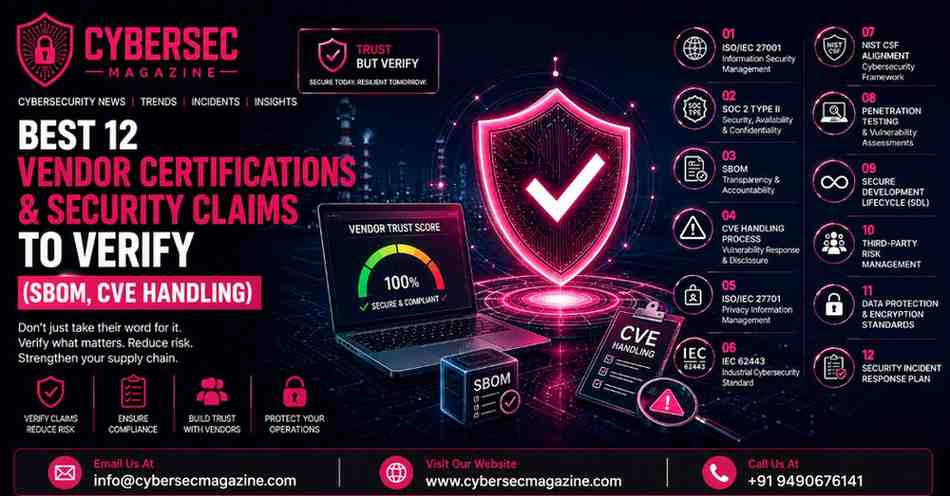
Best 12 Vendor Certifications & Security Claims to Verify
Vetting OT vendors in 2026? Learn the 12 essential security certifications, SBOM requirements, and CVE handling claims you must verify to ensure resilience. In 2026, the industrial landscape is defined by hyper-connectivity. As we integrate IIoT, cloud analytics, and advanced robotics into our Operational Technology (OT) environments, the “air-gap” has become a memory. However, this […]
12 Simple Fixes for Common PLC Vulnerabilities
Programmable Logic Controllers remain among the most critical, and most consistently under-hardened, assets in industrial environments. Despite years of ICS security guidance from CISA, NIST, and industry standards bodies, the same vulnerability classes appear in plant after plant: default credentials left active, engineering networks flat and accessible, remote access paths unsecured, and firmware versions unchecked. […]