
Top 12 OT Use Cases for Digital Twins & Their Hidden Security Risks
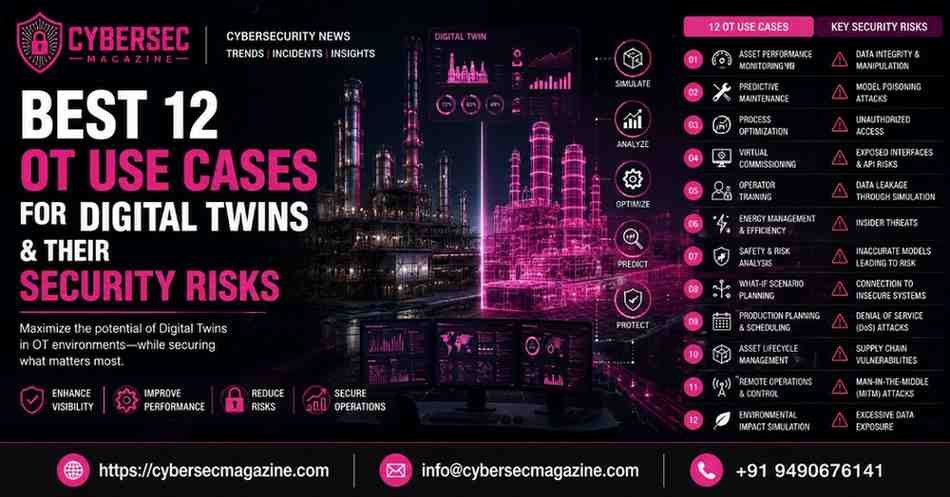
As a senior cybersecurity editor covering the high-stakes convergence of IT, Operational Technology (OT), and MIoT, I am witnessing a monumental shift in how we defend critical infrastructure. The global digital twin market is exploding, projected to jump from $18.9 billion in 2025 to over $26.4 billion in 2026, driven by an urgent need for asset optimization. By creating high-fidelity virtual replicas of physical environments, organizations report up to a 20% reduction in unexpected work stoppages and massive improvements in operational efficiency. These virtual sandboxes serve as consequence-free laboratories to conduct security testing, threat detection, and vulnerability management without ever endangering fragile legacy systems. However, this incredible innovation introduces a terrifying paradox: the very tool designed to protect your physical assets can easily become the ultimate weapon against them if breached. Below is our newsroom’s definitive breakdown of the top 12 use cases for digital twins in industrial environments, paired with the severe security risks they introduce.
Best 12 OT Use Cases for Digital Twins & their Security Risks
1. Consequence-Free Vulnerability & Patch Testing
Testing a new software patch directly on a live programmable logic controller (PLC) is a recipe for operational disaster, which is why security teams use digital twins as safe sandbox environments. Analysts can detonate malware, run aggressive vulnerability scans, and apply patches within the virtual replica to observe the outcomes without ever touching the fragile production line. The Security Risk: If an attacker breaches the digital twin and stealthily manipulates its telemetry (memory poisoning), they can trick the security team into validating a patch that actually introduces a backdoor. When that “validated” patch is pushed to the physical plant, the attackers gain immediate, authorized access to the core ICS environment.
2. Predictive Maintenance & Anomaly Detection
By ingesting massive streams of real-time sensor data, digital twins leverage machine learning to predict mechanical failures long before a pump or turbine actually breaks down. This predictive capability saves millions in unplanned downtime and extends the lifecycle of expensive heavy machinery by analyzing real-time data to optimize maintenance schedules. The Security Risk: The twin relies entirely on the integrity of the IoT telemetry feeding it. Adversaries can execute “sensor spoofing” attacks, feeding the digital twin false data that mimics mechanical degradation. This forces the plant into unnecessary, costly emergency shutdowns, or conversely, masks real physical damage until catastrophic equipment failure occurs on the factory floor.
3. Network Attack Path Visualization & Mapping
Digital twins excel at modeling complex OT network topologies across every layer of the Purdue Model, allowing SOC teams to visualize potential lateral movement paths. Defenders use this exact blueprint to see how a compromised corporate email account could eventually lead to a breached SCADA server through complex network architectures. The Security Risk: This comprehensive, perfectly accurate map of your entire operational network is the ultimate reconnaissance prize for an Advanced Persistent Threat (APT). If a nation-state actor exfiltrates the twin’s architectural data, they bypass months of noisy network scanning, gaining a perfect, undetected blueprint of your most critical physical vulnerabilities.
4. ICS Protocol Fuzzing & Command Validation
Security researchers actively use digital twins to test proprietary industrial protocols-like Modbus, DNP3, or OPC UA-by throwing malformed data packets at them (fuzzing) to discover zero-day vulnerabilities. The twin also validates that commands sent over these protocols adhere to expected, safe operational patterns before they reach physical devices. The Security Risk: An attacker who compromises the testing environment can reverse-engineer the twin’s responses to silently discover zero-day exploits before the defenders do. They essentially weaponize the organization’s own advanced testing environment, using the twin to craft the perfect, undetectable exploit for the physical machinery.
5. Automated Incident Response (IR) Playbooks
Modern digital twins simulate complex breach scenarios, allowing AI-driven agents to generate and test automated response playbooks without risking a massive plant shutdown. This allows security teams to validate containment strategies, such as dynamically isolating a compromised network segment or re-routing data flows, in real-time. The Security Risk: If the logic governing the digital twin is subtly altered by an insider or advanced malware, the automated playbooks might recommend disastrous actions. An AI agent relying on a poisoned twin could automatically shut down a critical cooling system during a fake anomaly, causing a real-world kinetic disaster based on fabricated insights.
6. Supply Chain & Third-Party Integration Modeling
Industrial organizations frequently use digital twins to simulate the integration of new third-party hardware or OEM software before allowing it onto the highly sensitive factory floor. This ensures that new components will not introduce unexpected latency, protocol mismatches, or compatibility issues that could disrupt continuous manufacturing processes. The Security Risk: The API connections required to feed external third-party data into the digital twin often lack strict zero-trust access controls. This provides a lucrative backdoor for supply chain attacks; attackers can infiltrate the digital twin via a weakly secured vendor API, subsequently pivoting across the IT/OT bridge into the corporate network.
7. Process-Tier Optimization & Setpoint Tuning
Process engineers utilize digital twins to safely experiment with control algorithms, setpoints, and thresholds-such as flow rates or boiler temperatures-to achieve maximum operational efficiency. It allows them to push systems to their theoretical limits in a virtual space before applying those highly optimized settings to physical PLCs. The Security Risk: A sophisticated “man-in-the-middle” (MitM) attack on the twin could subtly alter these optimization algorithms. When these poisoned, seemingly safe setpoints are pushed to the physical environment, they could slowly push machinery beyond its physical tolerances, causing severe mechanical wear or explosive failure over a period of months.
8. Cyber-Physical Red Teaming & Attack Simulation
Organizations can conduct full-scale red-team exercises on the digital twin, mimicking sophisticated, nation-state cyber-physical attacks (similar to Stuxnet) without any real-world fallout. This allows incident responders to practice defending against catastrophic events like a simulated total power grid failure or chemical spill in a consequence-free virtual laboratory. The Security Risk: The high-fidelity nature of these simulations means the twin holds highly classified data on the organization’s defensive capabilities and blind spots. If adversaries monitor these red-team exercises, they can analyze exactly how the SOC responds to specific threats, allowing them to design custom attacks that bypass known defenses.
9. Continuous Compliance & Regulatory Audit Validation
Digital twins are increasingly used to automate the arduous process of validating compliance against stringent frameworks like IEC 62443, NIS2, or NERC CIP. By running continuous automated checks against the virtual model, organizations can instantly generate compliance reports and prove their security posture to regulatory auditors without manual disruption. The Security Risk: Attackers can manipulate the compliance reporting dashboard within the digital twin to falsely report a secure, compliant state. This creates a dangerous illusion of security, lulling executives and regulators into a false sense of safety while a stealthy, persistent threat actively dismantles the physical plant’s actual defenses behind the scenes.
10. Workforce Training & Crisis Management Simulation
Digital twins provide highly immersive, deeply realistic virtual environments for training plant operators and security analysts in crisis management. New engineers can experience what a massive cyberattack on a turbine feels like, learning how to override digital controls and engage physical safety switches under intense pressure without risking real assets. The Security Risk: These specialized training environments often run on peripheral, less secure IT networks rather than the hardened OT core. If breached, attackers can observe operator behavior, learning human response times, standard operating procedures, and shift schedules to perfectly time a real-world cyber-physical attack when the team is most vulnerable.
11. Energy Grid Load Balancing & Dynamic Distribution
In the highly critical energy sector, digital twins model incoming weather patterns, historical peak usage, and regional load distribution to dynamically route power with maximum efficiency. This ensures that smart grids can handle the fluctuating demands of modern cities and renewable energy sources without suffering localized brownouts or transformer stress. The Security Risk: A synchronized cyberattack that feeds false meteorological data or fabricated demand spikes into the digital twin could cause the grid’s control logic to maliciously reroute power. This can instantly overload physical transformers, leading to cascading, wide-scale blackouts across regional critical infrastructure and endangering public safety.
12. MIoT Fleet & Healthcare Facility Management
In modern, connected hospitals, digital twins manage everything from the building’s HVAC systems to fleets of highly sensitive Medical IoT (MIoT) devices to ensure continuous patient safety. They monitor the operational health of MRI machines, infusion pumps, and critical environmental controls from a single, centralized virtual dashboard, streamlining facility management. The Security Risk: The massive hyper-connectivity required for a hospital digital twin means a single compromised edge sensor could provide a pivot point for a malicious actor. An attacker could exploit the twin to alter the HVAC environmental controls in intensive care units or spoof the calibration data of connected surgical equipment, directly endangering human lives.
Conclusion
Digital twins represent a profound paradigm shift in industrial cybersecurity, offering unparalleled visibility, predictive maintenance, and proactive defense capabilities that traditional security controls simply cannot match. As the market expands past $26 billion in 2026, adopting this technology will transition from a competitive advantage to a fundamental regulatory necessity for critical infrastructure operators. However, we must absolutely stop treating digital twins as mere IT monitoring tools or software dashboards. A high-fidelity digital twin is a Tier-1 cyber-physical asset that contains the exact blueprint to destroy your organization. If you do not secure the virtual replica with the exact same rigor, cryptographic trust, and zero-trust architecture as the physical plant, you are simply handing your adversaries the master keys to the kingdom. The future of industrial resilience relies on bridging the IT/OT divide safely-meaning your virtual defenses must be just as impenetrable as your physical ones.