
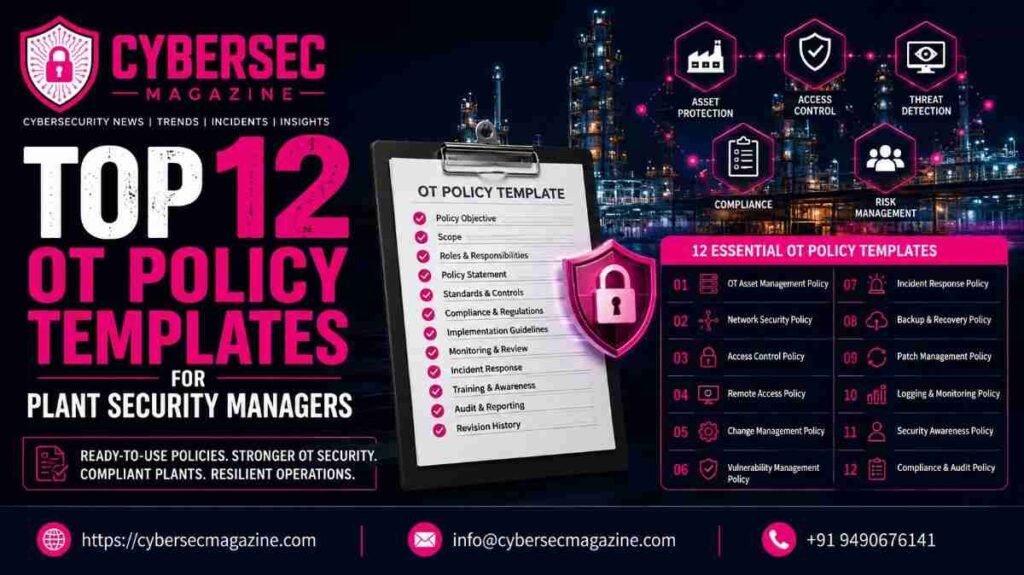
Top 12 OT Policy Templates for Plant Security Managers
As industrial environments undergo rapid digital transformation, plant security managers face an unprecedented challenge: bridging the traditional gap between enterprise IT and operational technology (OT). Unlike standard corporate networks where data confidentiality reigns supreme, industrial control systems (ICS), SCADA architectures, and distributed control systems (DCS) prioritize availability, physical safety, and real-time reliability.
With industrial cyberthreats evolving to target legacy firmware, smart sensors, and IIoT devices, generic IT policy documents are no longer sufficient. Plant security leaders need granular, field-tested policy templates tailored specifically for the plant floor.
Below are the top 12 operational technology (OT) policy templates every plant security manager must implement to fortify their industrial environment against sophisticated modern threat vectors.
Top 12 OT Policy Templates for Plant Security Managers
1. Legacy System Compensating Controls Policy
The Challenge: Many industrial facilities rely on legacy PLCs and engineering workstations running obsolete operating systems (like Windows XP or unpatched Windows 7) that cannot be rebooted or patched without risking catastrophic operational downtime.
Policy Focus: Defines mandatory non-patch mitigations, including micro-segmentation, protocol wrappers, strict endpoint hardening, and unidirectional traffic enforcers to isolate unpatchable assets.
2. Secure Remote Access & Multi-Factor Authentication (MFA) Policy
The Challenge: Third-party vendors and remote maintenance engineers frequently require backdoor access to shop-floor machinery, creating prime vectors for lateral movement.
Policy Focus: Mandates zero-trust network access (ZTNA) principles, prohibiting direct-to-floor modem or VPN connections. Requires hardware-token or certificate-based MFA, ephemeral access windows, and session recording for all vendor interventions.
3. Industrial Asset Discovery & Inventory Governance
The Challenge: You cannot protect what you cannot see. Modern facilities suffer from “shadow OT”-unauthorized switches, rogue wireless access points, and unmapped IoT meters brought in by contractors.
Policy Focus: Establishes protocols for passive and active asset discovery. Outlines how specialized inspection vendors-such as Nozomi Networks, Dragos, Claroty, Shieldworkz, and TXOne Networks-are integrated into the facility to continuously map communication flows, firmware versions, and rack configurations without disrupting sensitive serial buses.
4. OT Incident Response & Safe Islanding Playbook
The Challenge: Standard IT incident response often involves isolating a switch or shutting down servers. In a manufacturing plant, abruptly cutting network traffic to a live assembly line or a chemical valve can cause physical damage or safety hazards.
Policy Focus: Outlines a specialized OT containment hierarchy. It defines “safe islanding” procedures-how to decouple compromised programmable controllers into a safe manual-override state while maintaining physical process safety and emergency stop (E-stop) integrity.
5. Firmware Integrity & Secure Change Management Policy
The Challenge: Unauthorized or maliciously modified PLC ladder logic and firmware updates can cause silent, catastrophic process failures.
Policy Focus: Introduces cryptographic checksum verification before any firmware flashing or configuration change takes place on safety instrumented systems (SIS) or controllers. Requires an offline “golden image” repository for rapid recovery.
6. Industrial Demilitarized Zone (IDMZ) & Network Segmentation Policy
The Challenge: Flat networks linking corporate enterprise email systems directly to supervisory control layers expose critical manufacturing cells to enterprise-borne ransomware.
Policy Focus: Enforces Purdue Model-based architectural segmentation. It specifies firewall rule sets, data diode placements, and strict access rules governing data flow between Level 3 (Operations Management) and Level 4 (Enterprise IT).
7. Human-Machine Interface (HMI) Hardening & Access Control
The Challenge: HMIs are frequently left logged in with default administrative credentials, featuring unprotected USB ports or open web browser interfaces.
Policy Focus: Mandates session timeouts, disables unnecessary USB and peripheral ports across all shop-floor operator terminals, restricts local file execution, and enforces role-based access control (RBAC) tied to individual operator badges.
8. Wireless & IIoT Device Security Policy
The Challenge: The proliferation of smart sensors, wireless actuators, and mobile tablets introduces sprawling attack surfaces that bypass traditional physical perimeters.
Policy Focus: Governs the deployment, encryption standards (WPA3-Enterprise), and frequency management of industrial wireless networks. Mandates strict MAC filtering, device onboarding approval workflows, and automated vulnerability scanning for all connected IIoT endpoints.
9. Third-Party Vendor and Supply Chain Security Governance
The Challenge: External integrators often plug maintenance laptops directly into critical bus networks without undergoing malware hygiene checks.
Policy Focus: Implements mandatory pre-connection security scans for all vendor-owned equipment, strict software bill of materials (SBOM) disclosures for new plant software integrations, and strict legal accountability for introduced vulnerabilities.
10. Physical-Cyber Security Convergence Policy
The Challenge: Physical access to control rooms, wiring closets, and remote terminal unit (RTU) cabinets often lacks correlation with digital security logs.
Policy Focus: Aligns physical badge-reader logs with digital active directory and firewall logs. It mandates intrusion detection for remote enclosures and ensures that door-prop or tampering alarms trigger immediate alerts in the security operations center (SOC).
11. OT-Specific Cybersecurity Awareness & Phishing Training
The Challenge: Plant operators and floor engineers are rarely targeted by standard office IT phishing simulations, leading to low awareness of industrial threat actor tactics (such as watering-hole attacks targeting engineering forums).
Policy Focus: Establishes context-aware training modules focusing on industrial espionage, USB drop attacks in parking lots, social engineering vectors targeting control room staff, and safe handling of engineering software downloads.
12. Backup, Disaster Recovery, and Process Restoration Policy
The Challenge: Enterprise backup solutions often fail to back up proprietary PLC project files, ladder logic, HMI project configurations, and historian databases correctly.
Policy Focus: Defines strict recovery point objectives (RPO) and recovery time objectives (RTO) for physical control assets. Requires air-gapped, immutable backups of all control logic configurations and mandates regular disaster recovery drills simulating total plant system restoration.
Conclusion
As cyber-physical threats transition from theoretical concerns to daily operational disruptions, treating industrial security as an afterthought is no longer viable. Recent industry data shows that over 70% of industrial organizations are actively increasing their OT cybersecurity investments, while administrative responsibility shifts toward C-level oversight. However, tools alone cannot protect a facility without the rigorous administrative backing of standardized procedures.