
Top 10 Ways AI Is Being Abused Against OT (Threat Examples)
Welcome back to the cybersecurity desk. As an editor mapping the high-stakes convergence of IT, OT, and MIoT, I spend my days analyzing where sophisticated code meets physical infrastructure. Right now, a quiet revolution is rewriting the industrial threat landscape. We have spent years discussing how defenders can leverage machine learning for predictive maintenance and anomaly detection. But the other side of the ledger is scaling at a terrifying pace.
Generative AI and automated machine learning frameworks have fundamentally democratized high-complexity attacks. Recent industrial threat intelligence reveals that advanced adversaries are leveraging large language models and autonomous agents to compress multi-week reconnaissance and exploit development cycles down into mere minutes. In operational technology (OT)-where legacy systems, undocumented firmware, and flat networks still dominate-AI isn’t just a force multiplier; it is an aggressive accelerant.
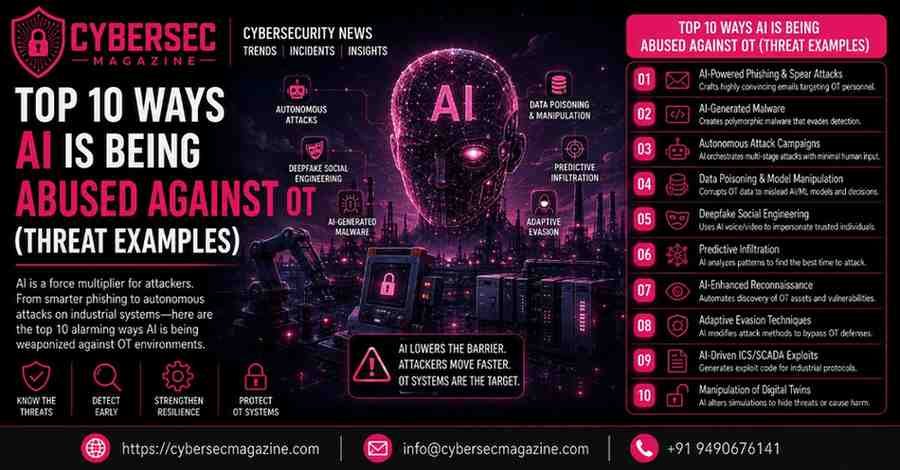
To defend the factory floor and critical infrastructure grids, we must look past generic IT threat models and examine how artificial intelligence is actively being weaponized against industrial control systems (ICS). Here are the top 10 ways AI is being abused against OT.
Top 10 Ways AI Is Being Abused Against OT (threat examples)
1. Autonomous Network Reconnaissance and Asset Mapping
Historically, mapping a complex OT environment required meticulous, slow manual active scanning that risked crashing fragile PLCs or setting off network intrusion detection systems. Threat actors are now deploying AI-driven OSINT and reconnaissance agents (such as customized LLM frameworks) to rapidly parse open-source intelligence, corporate GitHub repositories, and exposed Shodan endpoints. The AI instantly correlates fragmented data points to map out a target’s exact Purdue Model architecture, vendor equipment types, and remote-access gateways in seconds, allowing attackers to plan lateral movement from IT to OT with surgical precision before executing a single intrusive packet grab.
2. Hyper-Targeted, Context-Aware Industrial Spear-Phishing
Generic phishing emails are easy to spot, but AI engines can now ingest a company’s public communications, conference panel transcripts, and engineering job postings to craft hyper-personalized spear-phishing campaigns targeting specific plant engineers or SCADA administrators. By mimicking internal corporate language, vendor update protocols, or urgent maintenance schedules, AI generates text that successfully dupes personnel into handing over enterprise credentials or VPN access tokens-providing the initial foothold required to cross the IT/OT boundary.
3. Automated Vulnerability Discovery in Proprietary ICS Firmware
Industrial protocols and firmware binaries (like those running in Modbus gateways or specialized RTUs) are often proprietary and obfuscated, historically protecting them through “security through obscurity.” Threat actors are now feeding decompiled firmware binaries directly into AI models trained on code structure. The AI rapidly surfaces zero-day memory corruption flaws, logic bugs, and hardcoded backdoors across thousands of vendor firmware packages simultaneously, exponentially expanding the adversary’s zero-day arsenal against legacy industrial hardware.
4. Generative Exploit Code Generation for Legacy Protocols
Writing functional exploit code for industrial control protocols like DNP3, IEC 60870-5-104, or proprietary vendor APIs requires specialized engineering knowledge. Adversaries are using code-generation LLMs to translate technical protocol specifications directly into working exploit payloads. The barrier to entry for attacking industrial systems has collapsed; threat actors with minimal baseline knowledge of industrial automation can prompt an AI to generate functional exploit modules capable of injecting unauthorized register writes or crashing headless field devices.
5. AI-Assisted Prompt Injection for Data Exfiltration
As modern industrial plants adopt LLM-driven knowledge bases, maintenance assistants, and automated telemetry analyzers, attackers are targeting these interfaces via indirect prompt injection. By hiding malicious instructions inside routine maintenance logs, unverified sensor strings, or PDF equipment manuals ingested by Chubb-style plant AI assistants, attackers trick the internal LLM into exfiltrating proprietary production recipes, network topologies, and executive credentials out to an external command-and-control server.
6. Subversive Behavioral Mimicry (Evasion of AI Anomaly Detection)
Ironically, attackers are using machine learning models to study the very AI-driven anomaly detection tools deployed by defenders. By training generative adversarial networks (GANs) on normal industrial traffic patterns, attackers learn how baseline plant telemetry looks. Instead of launching loud, aggressive network scans that trigger immediate alarms, AI-assisted malware can dynamically throttle its communication speed, mimic standard polling intervals, and blend its data exfiltration into normal shift-change traffic patterns, effectively rendering itself invisible to standard behavior-based IDS.
7. Automated Credential Stuffing and Key Space Exploration
Default passwords, weak shared credentials, and predictable engineer naming conventions plague industrial environments. AI agents are deployed to automate credential-stuffing campaigns across exposed enterprise-facing portals that tie into industrial networks. The AI correlates leaked corporate credentials with industrial engineering logins, rapidly bypassing weak multi-factor authentication loops or legacy login panels to seize administrative control over remote telemetry gateways and HMIs.
8. Dynamic PLC Logic Mutation and Polymorphic Malware
Traditional industrial malware (like Stuxnet or Industroyer) relied on fixed logic payloads designed for specific hardware configurations. Today, attackers are experimenting with AI-driven metamorphic engines that dynamically rewrite PLC ladder logic and control scripts upon every infection cycle. Because the binary signature mutates continuously, signature-based security tools fail to recognize the threat. The malware adapts its internal routines to match the exact hardware model of the compromised controller it lands on, maximizing physical impact while evading host-based integrity monitoring.
9. AI-Driven Denial of Service (DoS) via Protocol Flooding
Industrial networks operate under strict deterministic timing constraints, where millisecond delays can disrupt continuous manufacturing processes. AI tools are used to calculate the exact frequency, packet size, and timing required to overwhelm industrial switches or controllers without triggering hard link failures. By flooding specific protocol ports with intelligent, non-signature traffic spikes, AI orchestrates targeted Denial of Service conditions that freeze HMI screens, delay safety controller heartbeats, and force operators blind during critical operational windows.
10. Synthetic Data Poisoning of Predictive Maintenance Models
Rather than breaking things with a sudden explosion, sophisticated actors are targeting the machine learning models that industrial plants rely on for predictive maintenance. By intercepting sensor feeds or compromising edge data pipelines, attackers inject subtle, long-term anomalies into the training data. The plant’s own predictive AI is systematically “poisoned” over months, causing it to misclassify severe mechanical wear as normal operating noise-or conversely, triggering false-positive emergency shutdowns that inflict massive financial losses and degrade equipment through thermal shock.
Conclusion
The convergence of artificial intelligence and operational technology has birthed a synthetic battlefield where speed, scale, and automation dictate survival. Attackers no longer need deep industrial engineering degrees to threaten a power grid or a manufacturing plant; they can rent or prompt AI models to do the heavy lifting of reconnaissance and exploit design. To counter this, industrial defenders must move beyond static perimeters and compliance checklists-embracing zero-trust architectures, immutable logging, hardware-anchored trust, and rigorous behavioral verification to ensure that the machines running our physical world cannot be outsmarted by synthetic adversaries.