
Top 10 Secure Edge-to-Cloud Architectures for OT Data
Welcome back to the cybersecurity desk. As an editor mapping the high-stakes convergence of IT, OT, and MIoT, I see a dangerous engineering friction point plaguing industrial enterprises everywhere. Corporate boards want real-time cloud analytics, predictive maintenance AI, and unified business intelligence dashboards. Meanwhile, plant managers and OT engineers are staring at fragile, legacy Programmable Logic Controllers (PLCs) that crash if scanned incorrectly, terrified that opening a path to the cloud will invite the next ransomware catastrophe.
The old “air gap” is long dead, flattened by the operational gravity of Industry 4.0. Recent industrial data shows that nearly 60% of manufacturing and critical infrastructure organizations suffered an operational technology security incident, with an overwhelming majority of vectors originating from poorly secured IT-to-OT data pathways. Simply bolting an enterprise IT firewall onto an industrial control system (ICS) is a recipe for physical disaster.
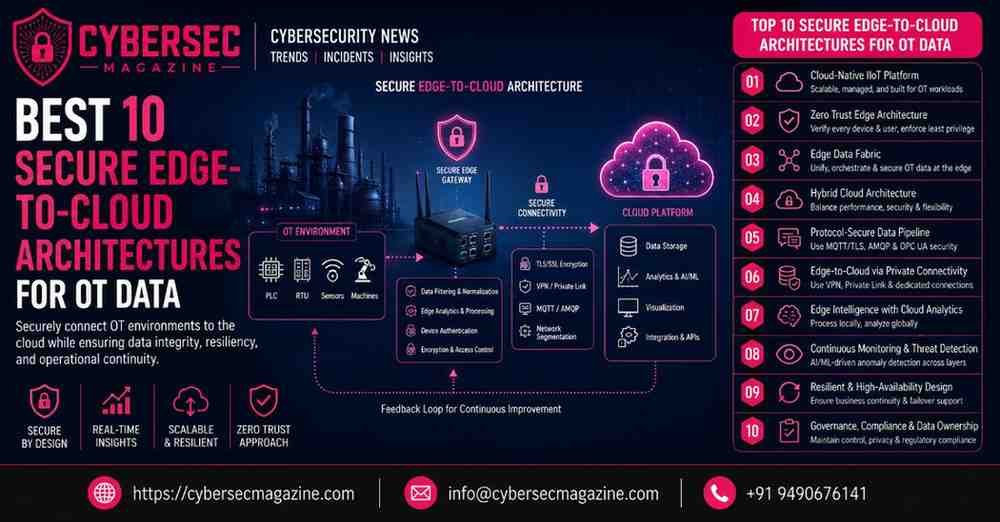
To safely bridge the factory floor and the cloud, you need purpose-built architectural patterns that guarantee data integrity, low-latency determinism, and zero lateral movement. Here are the top 10 secure edge-to-cloud architectures for OT data transformation.
Best 10 Secure Edge-to-Cloud Architectures for OT Data
1. Hardware-Enforced Unidirectional Gateways (Data Diodes)
Hardware-enforced unidirectional gateways, commonly known as data diodes, serve as the gold standard for high-consequence environments like nuclear facilities. This architecture utilizes physical optical components to allow telemetry to flow strictly out of the OT network to the cloud, while making it mathematically impossible for any inbound packets to cross the boundary. By guaranteeing absolute physical isolation of the control loop, organizations can feed live operational data into cloud analytics without ever exposing their sensitive core processes to external threats.
2. Protocol-Translating Edge Buffers (Industrial DMZ Gateways)
Protocol-translating edge buffers act as an essential security layer by creating an industrial demilitarized zone. Legacy industrial protocols like Modbus or DNP3 are inherently insecure and cannot be transported safely across the internet. By deploying a hardened edge gateway, you terminate raw traffic locally, perform deep packet inspection to strip unnecessary metadata, and repackage the telemetry into encrypted, lightweight MQTT streams. This buffer zone effectively shields your vulnerable field devices from direct exposure to the wider corporate network.
3. SASE-Compliant Industrial Edge Frameworks
Secure Access Service Edge (SASE) frameworks, adapted for industrial use, distribute security points of presence directly to the edge. Rather than backhauling traffic to a centralized corporate firewall, these frameworks evaluate device identity and posture locally at the machine level. This minimizes latency while ensuring that cloud-bound traffic undergoes inline inspection, effectively preventing lateral movement. By treating every edge node as a micro-perimeter, you maintain sub-millisecond response times essential for real-time control while enforcing rigorous cloud uplink security.
4. Zero Trust Network Access (ZTNA) Micro-Tunnels
Zero Trust Network Access (ZTNA) micro-tunnels represent a critical shift from legacy VPNs, which often grant dangerously broad network visibility. By replacing traditional tunnels with application-specific ZTNA micro-tunnels, you ensure that cloud-based analytics platforms can only access a specific edge container or historian endpoint, never the underlying PLC network. Every connection requires continuous, identity-based validation and device posture checking, ensuring that if a cloud credential is compromised, the attacker remains trapped within a single, isolated application path.
5. Mutual TLS (mTLS) with Hardware Roots of Trust
Mutual TLS (mTLS) with hardware roots of trust provides the foundational cryptographic identity necessary for secure cloud communication. This architecture mandates that every edge gateway utilizes a physical Trusted Platform Module (TPM) chip to store sensitive keys in tamper-proof silicon. Communication with the cloud is secured via strict mTLS, ensuring that both the edge node and the cloud broker verify each other’s unique X.509 certificates before a single byte of telemetry is transmitted, preventing man-in-the-middle impersonation.
6. Localized AI Anomaly Filtering at the Edge
Localized AI anomaly filtering at the edge drastically minimizes the cloud attack surface by processing raw data before transmission. Streaming massive volumes of unfiltered OT telemetry to the cloud consumes excessive bandwidth and increases interception risks. By deploying containerized machine learning models directly on ruggedized edge hardware, the gateway analyzes patterns of life and transmits only aggregated summaries, health attestations, or verified alerts. This architecture ensures that cloud platforms receive actionable intelligence without gaining access to raw, sensitive operational data.
7. Cryptographically Verified FIDO Device Onboarding
Cryptographically verified FIDO device onboarding solves the dangerous supply chain vulnerability of pre-configured edge nodes. By utilizing FIDO Device Onboard specifications, hardware remains neutral until its first power-on at the industrial site. The device automatically establishes an attested connection with the cloud management platform, verifying its unique identity through its TPM before downloading operational configurations. This zero-touch approach eliminates manual credential handling, ensuring that devices are securely provisioned without ever exposing master keys during transit or initial deployment.
8. Containerized Workload Sandboxing
Containerized workload sandboxing is vital when running multiple multi-vendor applications, such as security agents and local historians, on a single edge gateway. Leveraging secure, lightweight container runtimes like K3s with strict resource isolation ensures that applications operate in independent user spaces. If a cloud-connected analytics application is exploited by a sophisticated threat, the container boundary prevents the attacker from escalating privileges to the underlying operating system, effectively containing the breach and protecting the critical industrial network interfaces below.
9. Offline-Survivable Store-and-Forward Pipelines
Offline-survivable store-and-forward pipelines guarantee that industrial processes continue despite inevitable internet connectivity drops. This pattern incorporates encrypted local buffer storage on the edge gateway, allowing nodes to retain telemetry in a secure queue during WAN failures. Once connectivity is restored, the gateway securely flushes the backlog without risking data corruption or replay attacks. This architectural pattern is non-negotiable for modern IIoT, as it ensures that local safety interlocks and process monitoring remain functional regardless of cloud availability.
10. Immutable Decentralized Lineage Tracking
Immutable decentralized lineage tracking ensures that cloud-bound data has not been spoofed or manipulated in transit, which is critical for regulatory compliance under frameworks like NIS2. Every telemetry batch generated at the edge is cryptographically hashed and anchored using lightweight distributed ledgers. This creates an unalterable audit trail, proving the integrity of the data processed by cloud AI models. By validating the source and state of every packet, organizations build a transparent, verifiable chain of trust from sensor to cloud.
Conclusion
Connecting your operational technology data to the cloud is no longer a futuristic ambition-it is a mandatory driver for modern industrial competitiveness. However, treating cloud connectivity as a simple IT network extension invites catastrophic physical disruption. By implementing these secure edge-to-cloud architectures, industrial organizations can successfully harness the power of cloud analytics and AI without compromising the availability, integrity, or safety of the factory floor. Secure the edge, govern the pipeline, and bridge the IT/OT divide with absolute confidence.