
Top 10 OT Cloud Migration Security Pitfalls (and Mitigation)
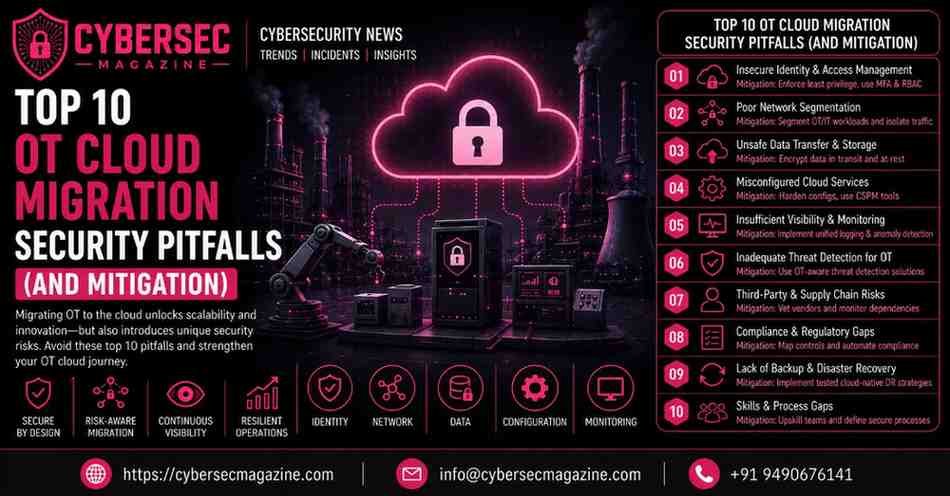
Industrial enterprises are accelerating cloud adoption to harness centralized telemetry analytics and predictive maintenance. However, migrating Operational Technology (OT) and Industrial Control Systems (ICS) beyond traditional air-gapped perimeters introduces severe cyber-physical vulnerabilities. With cloud misconfigurations and API blind spots driving nearly 45% of modern enterprise breaches, industrial security architects cannot rely on standard enterprise IT cloud playbooks.
Bridging the gap between physical plant safety and dynamic cloud services requires deep domain awareness. Below are the top 10 OT cloud migration security pitfalls, complete with field-tested mitigation strategies to protect critical infrastructure assets.
Top 10 OT Cloud Migration Security Pitfalls (and mitigation)
1. Treating OT Cloud Migration Like Standard Enterprise IT Lift-and-Shift
Applying generic IT cloud migration templates to industrial environments ignores the strict requirement for deterministic real-time communication and physical process safety. Treating programmable logic controllers (PLCs) like standard virtual machines often introduces dangerous network latency, disrupts safety instrumented systems (SIS), and creates direct cyber-attack paths into core machinery.
Mitigation: Establish a dedicated OT-to-Cloud architecture review board. Enforce a security-by-segmentation design phase where data flows from Purdue Model Level 0 through Level 3 are mapped before deployment, ensuring critical safety loops remain entirely isolated.
2. Blindly Trusting Cloud Provider Default Security Configurations
More than 31% of cloud security incidents stem from manual configuration errors and misunderstandings of shared responsibility frameworks. In an industrial context, leaving a cloud storage bucket or IoT ingestion broker misconfigured can expose raw sensor telemetry, plant blueprints, and command logs directly to the public internet.
Mitigation: Deploy automated Cloud Security Posture Management (CSPM) platforms tuned for industrial data models. Enforce strict Infrastructure-as-Code (IaC) templates that automatically block public-facing permissions on all industrial data lakes and APIs.
3. Inadequate Identity and Access Management for Third-Party Vendors
Industrial plants heavily rely on external system integrators, original equipment manufacturers (OEMs), and remote contractors for maintenance. With nearly 77% of organizations citing identity management as a primary cloud-native risk, unmonitored or over-permissioned vendor accounts represent a massive backdoor into connected OT systems.
Mitigation: Implement strict Zero Trust Network Access (ZTNA) combined with multi-factor authentication (MFA) and Privileged Access Management (PAM). Enforce session recording, just-in-time (JIT) access provisioning, and automated de-provisioning after maintenance windows close.
4. Flawed API Security and Unmonitored Ingestion Endpoints
APIs serve as the vital connective tissue for cloud-based Industrial IoT (IIoT) platforms, yet unsecured endpoints account for roughly 31% of cloud data leaks. Threat actors frequently exploit unauthenticated API gateways to execute injection attacks or harvest proprietary operational metadata across multi-tenant cloud ecosystems.
Mitigation: Treat every cloud API gateway as a high-risk perimeter. Implement token-based OAuth authentication, strict JSON schema validation, and runtime behavior monitoring to intercept anomalous payload requests before they reach field devices.
5. Exposing Unencrypted Telemetry in Transit and at Rest
Legacy industrial communication protocols (such as Modbus, DNP3, and OPC Classic) completely lack native encryption. When companies pipe this unencrypted data through standard internet tunnels or third-party brokers, attackers can easily intercept proprietary operational recipes or launch man-in-the-middle attacks.
Mitigation: Mandate end-to-end cryptographic protection across the entire pipeline. Encrypt all telemetry in transit using modern TLS 1.3 or secure virtual private networks from the edge gateway, and apply robust AES-256 encryption for all data at rest.
6. Severe Tool Sprawl and Cross-Domain Visibility Gaps
Approximately 69% of security professionals struggle with tool sprawl and visibility gaps when blending legacy on-premises assets with cloud services. When security operations centers (SOCs) cannot correlate cloud workloads with physical plant assets, silent lateral movement allows attackers to roam undetected.
Mitigation: Integrate cloud security telemetry with specialized OT asset discovery platforms (such as Claroty or Dragos). Build a unified SIEM pipeline that correlates cloud API audit logs directly with industrial network anomaly alerts.
7. Neglecting Edge-to-Cloud Latency and Fail-Safe Disruptions
Pushing heavy security inspection, deep packet analysis, or synchronous authentication checks directly into the real-time data path introduces unacceptable network jitter. In fast-moving manufacturing environments, high latency can cause control loops to timeout, triggering emergency shutdowns or physical damage.
Mitigation: Design edge-heavy, cloud-light hybrid topologies. Process time-sensitive telemetry and safety interlock logic locally at the industrial edge using containerized micro-engines, reserving the cloud asynchronously for macro-analytics and threat modeling.
8. Ignoring Software Bill of Materials and Container Vulnerabilities
Cloud-based industrial applications rely heavily on complex open-source libraries and container images. Unmonitored container repositories frequently host outdated packages carrying critical Common Vulnerabilities and Exposures (CVEs), introducing supply chain compromise vectors straight into the management plane.
Mitigation: Embed automated Software Bill of Materials (SBOM) generation and vulnerability scanning directly into your CI/CD pipelines. Continuously audit container registries and enforce automated patching schedules before code hits production cloud nodes.
9. Absence of Resilient Incident Response and Rollback Playbooks
Traditional IT disaster recovery plans often fail in OT because shutting down a compromised cloud gateway can inadvertently strand physical processes or lock out operators from emergency manual overrides. Poorly designed containment procedures risk compounding data corruption and downtime.
Mitigation: Build specialized cyber-physical incident response playbooks. Conduct regular tabletop exercises with IT security analysts and plant engineers to practice isolating cloud environments without cutting off local manual safety overrides.
10. Regulatory Non-Compliance and Data Sovereignty Missteps
Industrial sectors face stringent global regulations (including NERC CIP, NIS2, and IEC 62443) governing data residency, logging retention, and physical security. Storing critical infrastructure telemetry in unverified foreign cloud zones frequently results in heavy compliance violations and legal penalties.
Mitigation: Partner with cloud providers offering dedicated sovereign cloud infrastructure designed to meet local industrial data residency laws. Implement automated compliance validation tools to continuously audit cryptographic key management and regional data storage policies.
Conclusion
Migrating Operational Technology environments to the cloud unlocks massive scalability, predictive intelligence, and operational efficiency. However, the intersection of digital cloud code and physical machinery leaves zero margin for error. By proactively tackling these 10 security pitfalls-bridging IT-OT governance gaps, enforcing strict zero-trust identities, and prioritizing edge resilience-industrial organizations can safely navigate their cloud transformation while hardening critical infrastructure against sophisticated modern adversaries.