
Top 10 OT Blue Team Exercises to Build Resilience
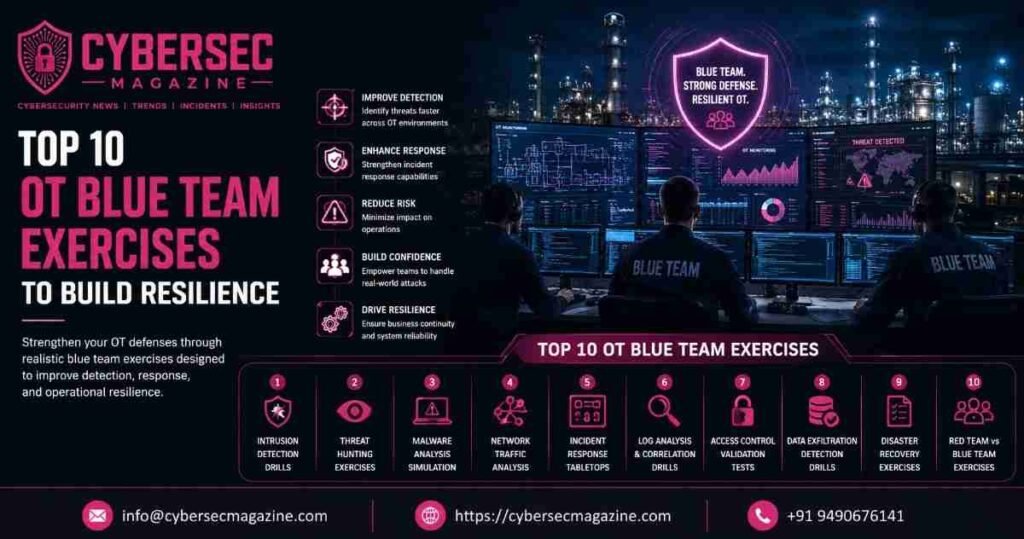
The digital transformation of Operational Technology (OT) and Industrial Control Systems (ICS) has redefined the modern cyber threat landscape. High-profile incidents targeting critical infrastructure-ranging from ransomware halting manufacturing operations to targeted APT campaigns altering SCADA process logic-have made one reality clear: traditional IT incident response playbooks fail when applied to OT environments. When an incident occurs across Purdue Levels 0 through 3, security operations centers (SOCs) cannot simply isolate endpoints or wipe infected servers without risking physical asset damage, worker safety hazards, or multimillion-dollar production outages. Building genuine cyber resilience requires defensive security teams (“Blue Teams”) to regularly validate their detection capabilities, incident response playbooks, and cross-functional coordination through realistic, OT-specific simulation drills. Based on threat intelligence, real-world incident forensics, and industrial red-teaming scenarios
Top 10 OT Blue Team Exercises to Build Resilience
1. The IT-to-OT Lateral Ransomware Spillover Simulation
Corporate IT ransomware frequently attempts to cross the Industrial DMZ into Manufacturing Execution Systems (MES) and Plant Control Networks, threatening critical production lines. Operating at Purdue Level 3.5 down to Level 2, this exercise simulates a compromised domain controller or spear-phishing entry point on the enterprise side. Blue Teams must detect unauthorized lateral movement attempts across iDMZ jump hosts, validate network conduit isolation, and execute emergency network severance procedures to halt infection propagation without crashing active physical processes.
2. Unauthorized PLC Ladder Logic Manipulation Drill
Attackers gaining access to field controllers often attempt to deploy modified control recipes, register overrides, or malicious ladder logic blocks. Targeting Purdue Level 1 controllers running protocols like Modbus/TCP or Siemens S7, this drill trains OT responders to identify malicious firmware updates and code changes pushed from compromised Engineering Workstations. Blue Teams must detect baseline deviations using passive deep packet inspection (DPI), capture forensic PCAP evidence, and safely restore known-good logic configurations without tripping safety instrumented systems (SIS).
3. Rogue Third-Party Vendor Remote Access Hijack
Third-party OEM field engineers and maintenance vendors routinely connect to plant systems via remote VPNs, jump boxes, and maintenance portals. Focusing on enterprise IT and Purdue Level 3.5 remote access gateways, red team injectors simulate an adversary hijacking legitimate vendor credentials or exploiting unpatched remote access portals during off-peak hours. Blue Teams must detect credential misuse, anomalous access times, or unauthorized internal port scanning, trigger step-up authentication, and terminate compromised sessions via zero-trust access control rules.
4. Sub-Fab & Industrial Facility Utility Sabotage
Threat actors frequently target secondary, non-process critical infrastructure such as HVAC, water treatment, toxic gas scrubbers, or power distribution to disrupt plant operations. Impacting Purdue Level 1 and 2 building automation and auxiliary systems, this exercise injects anomalous telemetry into Building Automation Systems (BAS) via BACnet or Modbus/TCP protocols to simulate forced temperature shifts, pressure drops, or tripped circuit breakers. Blue Teams must correlate secondary physical alarms with OT network alerts to distinguish between mechanical hardware failure and intentional cyber sabotage.
5. Rogue Wireless Drop-Box & Physical Intrusion Response
Plant floor environments remain vulnerable when physical security breaks down and unauthorized hardware devices are directly attached to local switches or serial gateways. Targeting Purdue Level 1 and 2 plant floor networks, a simulated insider or physical intruder connects a rogue cellular drop-box or unauthorized Wi-Fi access point to a spare Ethernet port on an unmanaged switch. Blue Teams must rapidly pinpoint the rogue MAC/IP address using passive asset discovery tools, execute port-level containment via NAC or physical switch isolation, and dispatch plant security to the physical cabinet location.
6. SECS/GEM & Industrial Protocol Command Injection
Unauthenticated, in-line industrial protocol command tampering can silently alter manufacturing parameters such as wafer etch times, chemical ratios, or conveyor speeds. Operating at Purdue Level 2 across Equipment Automation Programs and tool controllers, injectors generate unauthorized function calls across unencrypted industrial streams like SECS/GEM, EtherNet/IP CIP, or DNP3. Blue Teams must utilize protocol-aware intrusion detection systems (IDS) to catch command-level anomalies, verify process data integrity, and implement temporary protocol-filtering firewall rules.
7. GNSS Spoofing and Time Synchronization Tampering
Manipulation or jamming of precise time-synchronization sources (NTP/IEEE 1588 PTP) or GPS feeds destabilizes SCADA logs and automated control systems. Impacting Purdue Level 3 time servers, substation relays, and navigation feeds, this simulation introduces drifting clock times or manipulated GNSS coordinates into SCADA historians and sequence-of-events (SOE) recorders. Blue Teams must identify timing skew alerts, isolate compromised NTP sources, switch to internal atomic clock baselines, and re-synchronize time stamps across distributed event logs for accurate forensics.
8. HMI Spoofing & Operational Data Tampering
Blinding attacks manipulate operator consoles to display false normal process parameters while destructive physical conditions occur in the background. Targeting Purdue Level 2 Human-Machine Interfaces and operator consoles, this drill injects spoofed status data into the operator display while altering physical setpoints at the controller level. Blue Teams must cross-reference primary HMI readouts against out-of-band telemetry, secondary physical gauges, and raw historian logs to detect data integrity attacks before physical safety thresholds are breached.
9. Supply Chain & Malicious Firmware Update Injection
Backdoored firmware updates delivered through compromised vendor portals or technician USB drives pose severe supply chain risks to field controllers. Affecting Purdue Level 1 field device microcode and firmware, analysts simulate receiving a compromised firmware image during scheduled maintenance. Blue Teams are tasked with performing offline static binary analysis, verifying cryptographic checksums against trusted vendor repositories, and detecting unauthorized flash attempts on field hardware before execution.
10. Complete “Black Sky” Outage & Offline Forensics Drill
Severe cyber incidents can completely disrupt primary communication channels, cloud SIEM platforms, internet connectivity, and central domain services. Spanning Purdue Levels 0 through 4 across the entire enterprise architecture, this drill completely cuts off cloud-connected tools and corporate IT communications. Blue Teams must deploy out-of-band incident response kits, collect local forensic artifacts directly from offline PLCs, HMIs, and network TAPs, and execute physical manual recovery playbooks using paper-based documentation and satellite communications.
Conclusion
Building true cyber resilience in Operational Technology environments requires moving beyond passive compliance checklists and theoretical tabletop discussions. By routinely putting defenders through realistic, hands-on Blue Team exercises that mimic actual adversary tactics-from IT lateral movement to PLC logic tampering-industrial organizations can validate their detection technology, refine cross-functional incident response playbooks, and ensure operational safety when real-world threats strike.