
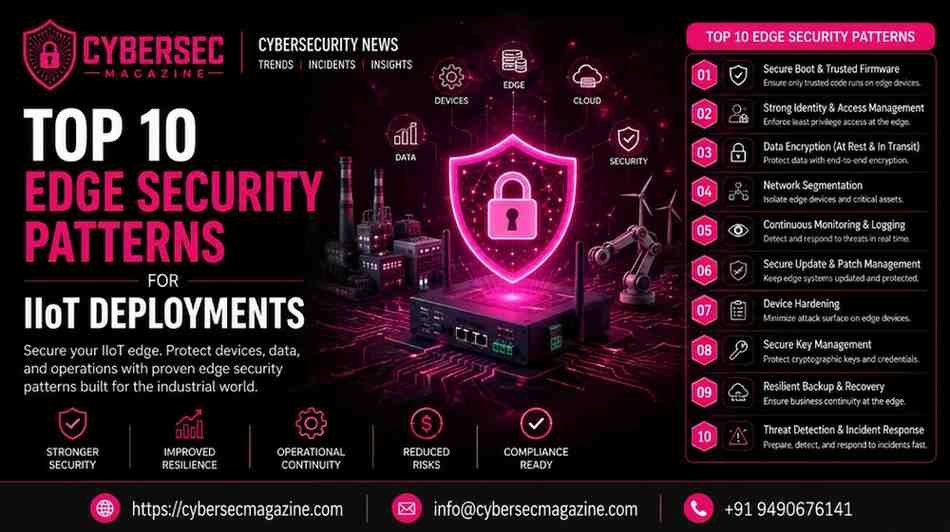
Top 10 Edge Security Patterns for IIoT Deployments
Welcome back to the cybersecurity desk. As an editor mapping the high-stakes convergence of IT, OT, and MIoT, I hear the same alarm bells ringing in every board room: We are pushing compute to the edge, but how do we secure it without breaking the factory floor?
In 2026, the Industrial Internet of Things (IIoT) is no longer a pilot project; it is the central nervous system of modern manufacturing, energy, and logistics. The IIoT technology market is projected to skyrocket to $751 billion this year, and hardware-specifically edge gateways and sensors-commands 55% of that massive spend. But with this unprecedented connectivity comes unprecedented risk. Threat actors are aggressively targeting the industrial edge, recognizing that a compromised enterprise laptop results in lost data, but a compromised IIoT gateway results in physical destruction, environmental disasters, and catastrophic production downtime.
Securing the IIoT edge requires fundamentally different architectures than traditional IT. Industrial lifespans stretch to 25 years, downtime tolerance is near-zero, and patching thousands of distributed devices simultaneously can trigger a facility-wide outage.
Top 10 Edge Security Patterns for IIoT Deployments
1. Hardware Root of Trust and Secure Boot
The edge is physically exposed. Unlike data center servers guarded by biometric locks, IIoT gateways often sit in remote, unmanned utility cabinets or along exposed pipelines.
- The Pattern: Devices must be engineered with a hardware Root of Trust (RoT), utilizing Trusted Platform Modules (TPM) to store cryptographic keys in isolated, tamper-proof silicon. Coupled with Secure Boot, this ensures the device cryptographically verifies the integrity of the operating system and firmware before booting. If a threat actor physically tampers with the device or flashes malicious firmware, the gateway simply refuses to start, effectively neutralizing the physical attack vector.
2. Containerized Workloads with Staged Rollouts
In OT environments, the riskiest security event isn’t always the vulnerability-it is often the patch. Pushing a fleet-wide firmware update can turn a minor fix into a multi-million-dollar outage.
- The Pattern: Transitioning from monolithic firmware to containerized edge workloads (using lightweight Docker or Kubernetes) drastically reduces this risk. By isolating applications, security teams can update a specific telemetry container without rebooting the core operating system or disrupting the control loop. Furthermore, updates must be orchestrated via staged rollouts with automated health-check gates, allowing instant rollback if a container fails on the edge node.
3. Edge-Native Protocol Translation
Legacy OT systems speak proprietary, unencrypted languages (like Modbus TCP, DNP3, or PROFINET) that were designed for reliability, not security. Exposing these protocols directly to the cloud is a catastrophic mistake.
- The Pattern: The edge gateway must act as an intelligent protocol translator. It actively terminates the vulnerable, cleartext industrial protocols locally and translates the telemetry into modern, highly encrypted formats (like mutual TLS-secured MQTT or HTTPS) before sending it upstream. This ensures that the vulnerabilities of legacy PLCs never bleed onto the internet or the wider IT network.
4. Micro-Segmentation and Industrial DMZs (IDMZ)
Flat networks allow ransomware to pivot seamlessly from a compromised corporate email straight to a Level 1 factory floor controller.
- The Pattern: Extending the Purdue Enterprise Reference Architecture to the IIoT edge requires deploying edge gateways as functional Industrial Demilitarized Zones (IDMZs). These gateways must enforce strict micro-segmentation, utilizing stateful firewalls to explicitly permit only required telemetry traffic while enforcing a default “deny-all” policy. They prevent direct IT-to-OT communication, forcing all traffic to terminate and undergo deep packet inspection (DPI) at the gateway.
5. Mutual TLS (mTLS) for Machine-to-Machine Identity
In an automated factory, humans aren’t the primary users-machines are. Relying on static passwords, shared secrets, or long-lived API keys for M2M authentication creates a massive vulnerability for credential harvesting.
- The Pattern: Organizations must deploy Mutual Transport Layer Security (mTLS) across the IIoT edge. mTLS requires both the edge device and the cloud receiving server to mathematically verify each other’s cryptographic certificates before a connection is ever established. This identity-based access control prevents rogue devices or spoofed sensors from injecting falsified telemetry into your predictive maintenance algorithms.
6. Localized Anomaly Detection and AI Baselines
Sending massive volumes of raw OT data to a centralized cloud SIEM introduces unacceptable latency and wastes bandwidth. Furthermore, relying entirely on cloud-based analytics leaves the plant blind if internet connectivity drops.
- The Pattern: AI-driven threat detection must be pushed down to the edge gateway. These localized monitoring tools utilize machine learning to establish behavioral baselines of the specific machine cell they oversee. By analyzing flow metadata locally, they can instantly flag anomalous command injections or telemetry drift and trigger automated quarantine protocols at machine speed, completely independent of cloud connectivity.
7. Unidirectional Gateways (Data Diodes)
For the most critical infrastructure-such as nuclear power generation or toxic chemical refining-even the best software firewalls cannot provide a 100% guarantee against remote cyber-physical sabotage.
- The Pattern: Organizations are increasingly deploying hardware-enforced unidirectional gateways, or data diodes, at the edge. These physical devices utilize optical isolators to allow telemetry data to flow out of the OT network to the cloud, while making it mathematically and physically impossible for any data or commands to flow back in. This guarantees that no remote attacker can manipulate the physical process, regardless of their sophistication.
8. Zero Trust Network Access (ZTNA) for Remote Maintenance
Third-party original equipment manufacturers (OEMs) require remote access to maintain industrial machinery. Historically, this meant handing out broad VPN access that exposed the entire factory floor to a compromised vendor laptop.
- The Pattern: The edge gateway must serve as a ZTNA enforcement node. When a vendor requires access, they authenticate through a central broker using phishing-resistant MFA. The edge gateway then establishes an encrypted, time-bound tunnel directly to the specific asset under maintenance. This granular, least-privilege approach eliminates lateral movement capabilities and provides an undeniable audit trail of all vendor commands.
9. Dynamic Software Bill of Materials (SBOM) Enforcement
As adversaries increasingly target nested open-source libraries, supply chain poisoning has become a primary attack vector. If a compromised container image is pushed to the edge, the entire production line is compromised.
- The Pattern: IIoT deployments must integrate dynamic SBOM validation at the edge. Before a containerized application is allowed to execute on the gateway, the system cryptographically checks the image signature against the approved SBOM registry. If the hash does not match, or if a newly disclosed zero-day vulnerability is detected in the dependencies, the gateway automatically blocks execution and alerts the SOC.
10. Offline Survivability and Local Failback
Industrial networks are subjected to harsh conditions, and cloud connectivity is never guaranteed. If a cloud-based authorization server goes down, the factory floor cannot afford to grind to a halt.
- The Pattern: Security policies must be designed for offline survivability. Edge gateways must cache critical Identity and Access Management (IAM) policies, cryptographic keys, and routing rules locally. If the WAN link fails, the gateway enters a “local failback” mode, seamlessly enforcing micro-segmentation and localized threat detection to ensure the physical process continues to run securely without cloud oversight.
Conclusion
The convergence of IT and OT networks is no longer a future concept; it is the current reality of the industrial edge. As we deploy millions of IIoT sensors to drive predictive maintenance and AI-driven efficiency, relying on legacy IT firewalls and flat networks is a recipe for physical disaster. By adopting these 10 advanced edge security patterns-from hardware root of trust to strict containerized workloads-organizations can confidently harness the power of the Industrial Internet of Things without sacrificing the safety, availability, and integrity of their critical infrastructure. Secure the edge, and you secure the enterprise.