
Top 10 Differences: NIST CSF vs IEC 62443 for OT Operators
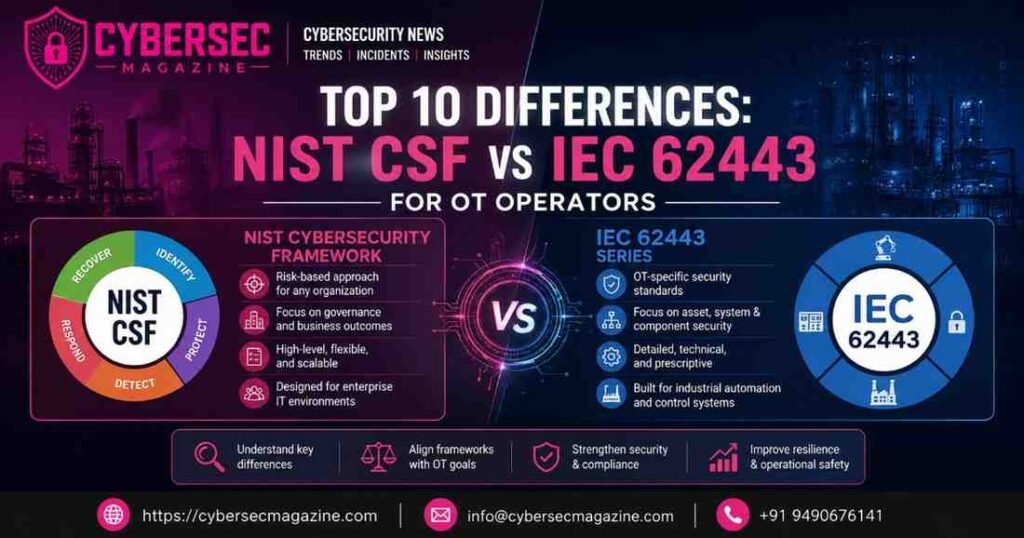
When industrial security leaders and Operational Technology (OT) operators sit down to map out a defense strategy, they almost invariably face a pivotal architectural crossroad: Should we align with the NIST Cybersecurity Framework (CSF) or the IEC 62443 standard series?
In an IT environment, a cyber breach results in data leakage or administrative disruption. In an OT environment, a security compromise can trigger physical destruction, environmental catastrophes, or loss of human life. Because these two frameworks originate from entirely different design philosophies-one built for enterprise-wide risk governance and the other engineered specifically for industrial control systems (ICS)-treating them as interchangeable options is a dangerous mistake.
Understanding the structural, technical, and operational differences between NIST CSF and IEC 62443 is vital for building a resilient, audit-ready industrial defense. Below are the top 10 core differences every OT operator must understand.
Top 10 Differences: NIST CSF vs IEC 62443 for OT Operators
1. Fundamental Scope and Domain Origin
- NIST CSF: Developed by the U.S. National Institute of Standards and Technology, NIST CSF is a general-purpose, enterprise-wide risk management framework. It applies broadly across commercial IT, financial systems, government agencies, and hybrid cloud infrastructures, requiring broad customization to address plant-floor realities.
- IEC 62443: Co-developed by the International Society of Automation (ISA) and the International Electrotechnical Commission (IEC), this standard series is built exclusively for Industrial Automation and Control Systems (IACS). Every sub-standard is written with operational continuity, physical safety, and real-time controller constraints in mind.
2. Prescriptive Technical Depth vs. Outcomes-Focused Agility
- NIST CSF: Operates primarily as an outcomes-focused framework. It dictates what high-level security objectives an organization must achieve (e.g., assets are identified, anomalies are detected) but intentionally leaves the how up to the organization’s risk-based judgment.
- IEC 62443: Highly prescriptive. It defines exact technical control requirements at both the system level (IEC 62443-3-3) and component level (IEC 62443-4-2), establishing precise expectations for protocol parsing, password complexity, and session timeouts on field-level devices.
3. Supply Chain and Ecosystem Stakeholder Differentiation
- NIST CSF: Version 2.0 incorporates expanded supply chain risk management categories, but it treats the enterprise largely as a unified entity facing third-party vendors.
- IEC 62443: Explicitly splits responsibilities across the entire industrial ecosystem. It places distinct, complementary obligations on Asset Owners (IEC 62443-2-1), System Integrators (IEC 62443-2-4), and Component Product Vendors (IEC 62443-4-1/4-2), ensuring that third-party hardware and software are secure by design.
4. Certification Pathways and Audit Verification
- NIST CSF: Is not a certifiable standard. It functions as a self-assessment maturity model and governance benchmark, meaning organizations cannot achieve official, third-party “NIST CSF Compliance certification”.
- IEC 62443: Features formal, internationally recognized compliance and certification pathways. Third-party testing agencies can formally audit and certify industrial control products, control systems, and plant integration processes against strict security levels.
5. Network Architecture Frameworks (Purdue Model vs. Universal Functions)
- NIST CSF: Relies on high-level protection categories that do not natively mandate a specific network architecture, leaving engineers to map out zone isolation independently.
- IEC 62443: Introduces the rigorous Zone and Conduit model (IEC 62443-3-2). It requires operators to formally segment plants into security zones based on criticality and control data flow through secure conduits, mapping directly onto the Purdue Enterprise Reference Architecture.
6. Quantification of Defense Posture (Security Levels vs. Maturity Tiers)
- NIST CSF: Measures progress using implementation tiers (Tiers 1 through 4) that evaluate how integrated risk management is into overall organizational culture and governance processes.
- IEC 62443: Quantifies technical resilience using Security Levels (SL 1 through SL 4). These levels define specific resistance thresholds against varying adversary capabilities, ranging from casual electronic misbehavior to sophisticated nation-state actors targeting critical infrastructure.
7. Integration with Advanced OT Visibility and Security Platforms
- NIST CSF: Provides broad guidance for detecting anomalies, but relies on general security tools without specifying deep industrial protocol parsing.
- IEC 62443: Demands continuous monitoring and auditing mechanisms capable of inspecting proprietary industrial protocols (such as Modbus, DNP3, and PROFINET). Modern industrial security platforms like the Shieldworkz OT Security & Forensic Platform bridge this requirement by delivering automated asset discovery, continuous posture monitoring, and compliance validation tailored directly to IEC 62443 security levels without risking plant availability.
8. Handling of Legacy Hardware and Unpatchable Assets
- NIST CSF: Recommends standard vulnerability management and patching lifecycles, which can cause severe operational friction when applied to legacy PLCs that cannot be rebooted or patched.
- IEC 62443: Explicitly addresses legacy industrial constraints by providing frameworks for compensating controls, network micro-segmentation, and VEX (Vulnerability Exploitability eXchange) workflows when patching is physically or commercially impossible.
9. Executive Reporting Language vs. Plant-Floor Engineering Execution
- NIST CSF: Built with boardrooms, CISOs, and executive leadership in mind. Its six core functions (Govern, Identify, Protect, Detect, Respond, Recover) provide a common corporate language for budgeting, risk profiling, and regulatory reporting.
- IEC 62443: Built for control engineers, automation technicians, and system architects. It provides the technical specifications needed to configure industrial firewalls, harden firmware, and specify secure controller procurement requirements.
10. Geographic Harmonization and Regulatory Mandates
- NIST CSF: Heavily favored within U.S. critical infrastructure sectors, federal contracting, and insurance frameworks, though its global influence continues to expand.
- IEC 62443: Serves as the preeminent global international standard, deeply integrated into European Union directives (such as NIS2) and international industrial safety regulations, making it essential for multinational corporations.
Conclusion
Viewing NIST CSF and IEC 62443 as an either-or proposition is a critical strategic error. In practice, elite industrial security programs harmonize both frameworks: use NIST CSF 2.0 as the governance front-door to communicate risk, secure executive buy-in, and report posture to company boards, and deploy IEC 62443 as the technical engineering backbone to secure plant floors, define zones and conduits, and harden industrial control systems against sophisticated cyber threats.