
Top 10 Concerns with LLMs and Industrial Knowledge Bases
Welcome back to the cybersecurity desk. As an editor tracking the high-stakes convergence of IT, OT, and MIoT, I am watching a massive paradigm shift unfold on the factory floor. Every major industrial player is rushing to integrate Large Language Models (LLMs) into their operations. The pitch is undeniably attractive: ingest decades of proprietary maintenance logs, SCADA manuals, and incident response playbooks into a centralized “Industrial Knowledge Base,” and let an AI assistant instantly guide your engineers through complex troubleshooting.
While LLMs can drastically reduce downtime and assist in correlating complex security events across IT and OT segments, the rush to deployment is outpacing our security frameworks. The integration of probabilistic AI into deterministic industrial control systems creates unprecedented attack surfaces.
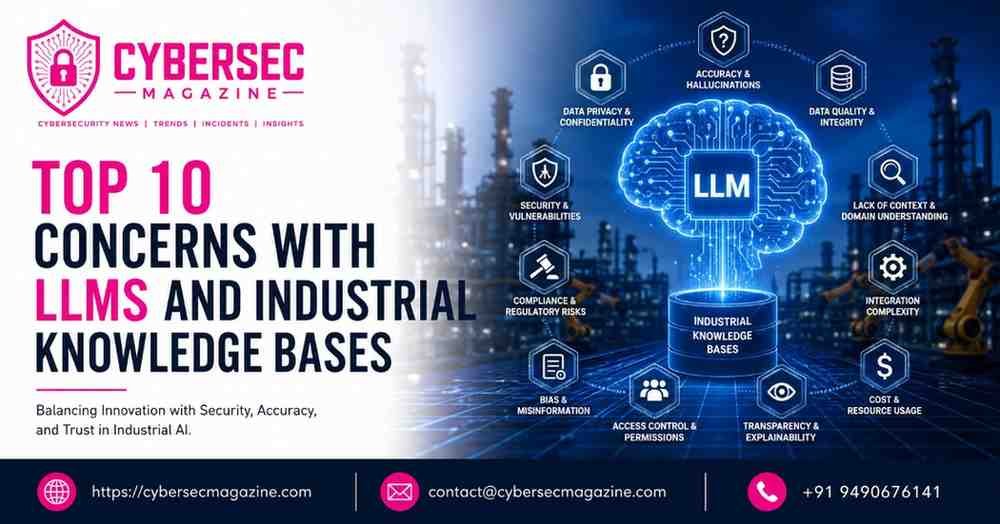
If you are building or deploying an LLM-driven industrial knowledge base, here are the top 10 cybersecurity concerns you must address before that system is allowed to interact with your production environment.
Top 10 Concerns with LLMs and Industrial Knowledge Bases
1. Prompt-to-Physical Attack Vectors
In a traditional IT environment, a successful prompt injection might result in unauthorized data access or a bypassed content filter. In an OT environment, if your LLM is integrated directly with your control systems or orchestration APIs, a crafted prompt could theoretically be translated into a physical command. The concept of “prompt-to-physical” attacks means an adversary could use natural language to trick the model into issuing a firmware update command to a Safety Instrumented System (SIS) during a live production run.
2. Hallucinations During Critical Incident Response
Industrial control systems require absolute determinism-if an engineer opens a valve, they need to know exactly what will happen. LLMs, however, are inherently probabilistic. If an operator asks the knowledge base how to stabilize a cascading pressure failure, and the model “hallucinates” a technically plausible but fundamentally incorrect procedure, the results could be physically catastrophic. Relying on unverified AI outputs during a crisis introduces an unacceptable level of operational risk.
3. Data Poisoning of the Industrial Knowledge Base
An LLM is only as reliable as the data it trains on. Adversaries who gain low-level access to your network don’t need to deploy ransomware immediately; instead, they can subtly alter the historical maintenance logs, network schematics, or safety manuals that your knowledge base ingests. This “data poisoning” slowly degrades the model’s accuracy over time, eventually causing the AI to recommend unsafe operational parameters or ignore critical telemetry alerts.
4. Model Inversion and Intellectual Property Leakage
Your industrial knowledge base likely contains the most sensitive data in your organization: proprietary manufacturing recipes, exact network topologies, and undocumented legacy system configurations. Attackers can use sophisticated “model inversion” techniques-submitting highly specific, targeted queries-to force the LLM into regurgitating this classified training data. This transforms your internal AI assistant into a highly efficient espionage tool for competitors or nation-state actors.
5. Autonomous Generation of Novel ICS Attacks
The same analytical power that allows an LLM to find obscure troubleshooting solutions can be weaponized. Threat actors are already leveraging LLMs to rapidly analyze massive volumes of ICS documentation and discover novel, non-obvious physical invariants and attack patterns. By interacting with a compromised internal knowledge base, an attacker can ask the AI to generate hyper-specific, automated attack sequences tailored exactly to your unique Purdue Model architecture.
6. Blurring the IT/OT Micro-Segmentation
For an industrial knowledge base to be truly effective, it often requires real-time telemetry from the plant floor combined with IT data (like active directory logs). Bridging this gap often requires the LLM’s backend to straddle the IT/OT boundary. If the AI’s API endpoints are compromised, adversaries can use the knowledge base as a covert bridge, bypassing your industrial Demilitarized Zone (DMZ) to move laterally from the corporate network directly into the control layer.
7. Over-Reliance and Automation Bias
A significant vulnerability is human psychology. As junior engineers increasingly rely on the LLM to quickly resolve complex OT alerts, they may develop “automation bias”-blindly trusting the AI’s output without independently verifying it against the physical realities of the plant. If the model fails or is compromised, the human operators may lack the deep, unassisted technical expertise required to safely operate the facility manually.
8. Privilege Escalation via the AI Agent
If the LLM is deployed as an active agent (capable of taking actions rather than just providing text), it must operate with specific network privileges. A common flaw is granting the AI excessive, “catch-all” permissions to ensure it can access all necessary databases and APIs. An attacker who compromises the LLM interface can hijack these high-level service accounts, utilizing the AI’s own privileges to execute commands or exfiltrate data they couldn’t access directly.
9. Vulnerabilities in RAG (Retrieval-Augmented Generation) Pipelines
Most industrial knowledge bases use RAG to fetch the most up-to-date documents before generating an answer. The security of this system depends entirely on the access controls of the vector database and the retrieval APIs. If the RAG pipeline does not enforce strict identity and access management (IAM), an unprivileged user on the factory floor could ask the LLM a question and inadvertently retrieve highly classified administrative credentials or executive data that the model fetched from an unsecured repository.
10. Lack of Deterministic Safety Guardrails
Standard IT security tools cannot adequately monitor LLM behavior because natural language is infinitely variable. You cannot write a simple firewall rule to block a “malicious sentence.” Deploying LLMs in OT requires complex, independent output verification systems-essentially, a deterministic safety net that mathematically verifies the AI’s recommendations against hardcoded physical constraints before any action is recommended to the human operator.
Conclusion
Integrating Large Language Models into your industrial knowledge base is not just another software upgrade; it is the introduction of a probabilistic reasoning engine into an environment that demands absolute certainty. While the efficiency gains in anomaly detection and incident triage are undeniable, they cannot come at the cost of your core safety instrumented systems. By strictly isolating AI agents, enforcing rigorous human-in-the-loop validation, and securing your training pipelines against data poisoning, you can harness the power of generative AI without handing adversaries the keys to your critical infrastructure.