
Best 12 Ways to Build an Industrial SBOM Program (Hardware + Firmware)
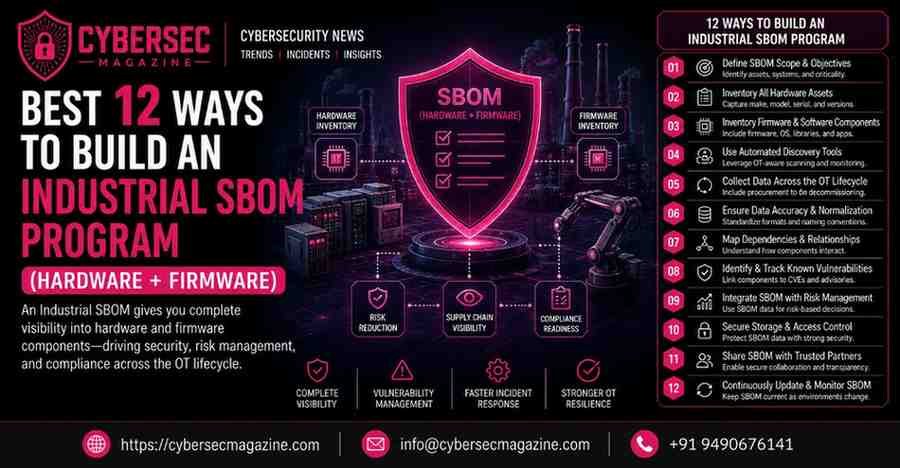
Building an effective Software and Hardware Bill of Materials (SBOM / HBOM) program for Operational Technology (OT) and Industrial Control Systems (ICS) is fundamentally different from managing standard enterprise IT supply chains. Industrial assets combine complex, proprietary silicon, heterogeneous Real-Time Operating Systems (RTOS), and deeply embedded custom firmware that must maintain ultra-high availability. When a zero-day vulnerability like Log4j or an embedded bootloader flaw hits a programmable logic controller (PLC), asset owners cannot simply reboot or hotfix production lines.
Industrial security leaders must establish rigorous, multi-layered transparency programs that map everything from microchips to the upper-layer SCADA supervisory software. Below are the top 12 expert strategies to successfully build and scale an industrial SBOM program that bridges both hardware and firmware constraints.
Best 12 Ways to Build an Industrial SBOM Program (hardware + firmware)
1. Unify Hardware and Firmware Component Inventories
Traditional IT SBOM frameworks focus almost exclusively on application dependencies and open-source packages. In OT environments, security begins at the silicon level. Your program must integrate Hardware Bill of Materials (HBOM) data-capturing microcontrollers, FPGAs, ASICs, and cryptographic chips-alongside firmware manifests. Tracking these physical root-of-trust components ensures you can instantly trace supply chain compromises stemming from counterfeit chips or tainted semiconductor supply lines.
2. Standardize on Machine-Readable Formats (CycloneDX vs. SPDX)
Avoid ad-hoc spreadsheets or static PDFs that quickly drift out of alignment with deployed assets. Standardize your pipeline around machine-readable schemas like CycloneDX or SPDX, which support deep hierarchical nesting and cryptographic component hashes. CycloneDX, in particular, offers robust extensions for IoT and industrial profiles, allowing automated tools to parse relationships between physical hardware modules, board support packages (BSPs), and executing firmware binaries.
3. Implement Automated Binary Analysis for Legacy ICS Devices
Most legacy PLCs, RTUs, and distributed control system (DCS) nodes lack native SBOM generation capabilities, and vendors rarely supply source code. Overcome this blind spot by deploying automated binary static analysis and firmware reverse-engineering pipelines. These tools unpack proprietary container formats, extract kernel modules, identify embedded open-source libraries (e.g., BusyBox, OpenSSL implementations), and automatically generate accurate component manifests from compiled binaries.
4. Bridge the IT-OT Governance Gap via Unified Repositories
OT cybersecurity programs fail when SBOM data remains trapped in isolated engineering silos. Establish a centralized SBOM system of record (SoR) that bridges enterprise IT repositories with plant-floor asset management tools. By integrating SBOM management platforms with your existing CMDB and industrial asset discovery tools (such as Claroty or Dragos), you gain real-time visibility into which physical controllers are running vulnerable firmware versions.
5. Enforce Strict Vendor Procurement Clauses and Contractual SLAs
Do not wait until procurement is finalized to ask for supply chain transparency. Update all vendor RFPs and procurement contracts to mandate the delivery of machine-readable SBOMs and HBOMs as a strict prerequisite for deployment. Require suppliers to update manifests within 48 hours of releasing a firmware patch or addressing a critical Common Vulnerabilities and Exposures (CVE) identifier across industrial network architectures.
6. Map Deep Transitive Dependencies and Build Context
Industrial firmware is rarely written from scratch; it relies heavily on deeply nested third-party RTOS kernels, communication stacks (e.g., Modbus, PROFINET, OPC UA libraries), and proprietary cryptographic modules. Your program must map both direct and transitive dependencies. Knowing that a vulnerable TCP/IP stack is buried three levels deep inside a smart meter’s communication card prevents catastrophic blind spots during incident response triage.
7. Integrate Vulnerability Exploitability eXchange (VEX) Workflows
An industrial SBOM without context triggers endless alert fatigue. Because many industrial components bundle vulnerable code that is functionally unexploitable due to air-gapped network configurations or disabled execution flags, you must pair your SBOM program with VEX (Vulnerability Exploitability eXchange) documents. VEX acts as a security advisory clarifying whether your specific asset is actually impacted by a known CVE, saving engineering teams from unnecessary, high-risk emergency patches.
8. Establish Secure Cryptographic Signing and Provenance Verification
Industrial supply chains are prime targets for sophisticated adversary tampering and nation-state firmware injection attacks. Implement robust cryptographic signing (using mechanisms like Sigstore or hardware security modules) for every generated SBOM and firmware image. Verifying component cryptographic hashes at the edge ensures that field controllers only execute verified, tamper-evident code updates across remote substation networks.
9. Tailor Access Control and Redaction Policies for Intellectual Property
Industrial automation vendors are frequently protective of their proprietary firmware recipes, device logic, and trade secrets. Build a flexible SBOM program that utilizes role-based access control and smart redaction policies. This allows vendors to obscure proprietary core logic while still exposing necessary structural dependency and vulnerability data to asset owners, resolving the tension between commercial confidentiality and operational safety.
10. Automate Continuous Monitoring Against Live Threat Feeds
An SBOM is a point-in-time snapshot that immediately decays the moment a new vulnerability is discovered. Integrate your industrial SBOM repository with continuous threat intelligence feeds and automated vulnerability scanners. Establish automated pipelines that cross-reference component versions against the National Vulnerability Database (NVD) in real time, instantly alerting security operations centers when a newly disclosed zero-day affects plant-floor assets.
11. Coordinate Change Management with Safety Instrumented Systems (SIS)
Unlike IT applications where continuous deployment is standard, pushing changes to industrial control systems requires strict adherence to safety lifecycles (e.g., IEC 61508/62443). Integrate your SBOM vulnerability triage workflows directly with plant change management and safety committees. This ensures that firmware updates and dependency patches identified through SBOM insights are rigorously tested in staging environments before risking unexpected process shutdowns.
12. Conduct Periodic Maturity Assessments and Tabletop Drills
Building an industrial SBOM program is an iterative maturity journey rather than a one-time project. Leverage frameworks like the CISA SBOM maturity model to evaluate your program annually across governance, generation depth, and sharing capabilities. Run simulated supply chain incident drills-such as tracing a compromised third-party driver across every connected PLC-to test the speed, accuracy, and resilience of your component tracking workflows.
Conclusion
As operational technology environments embrace smart manufacturing, IIoT, and advanced edge computing, the traditional perimeter defense model is no longer sufficient. Implementing a robust Industrial SBOM program that covers both hardware and firmware provides the vital transparency needed to navigate modern supply chain threats. By shifting from reactive firefighting to proactive, cryptographic asset visibility, industrial security leaders can ensure continuous operational resilience, protect critical infrastructure, and safeguard the physical world against sophisticated cyber attacks.