
Best 12 Steps to Prepare for an IEC 62443 Audit
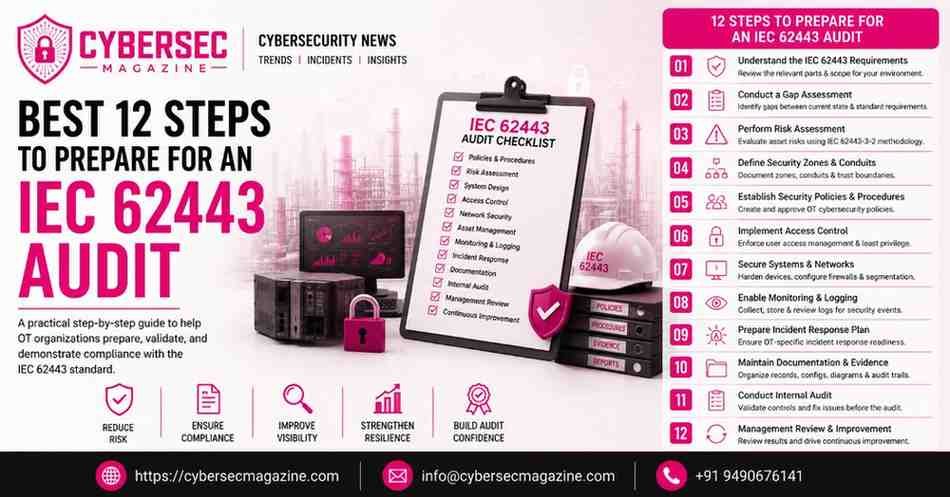
Preparing for an ISA/IEC 62443 compliance audit across Operational Technology (OT) and Industrial Control Systems (ICS) requires a distinct departure from traditional enterprise IT auditing frameworks. While corporate IT audits focus primarily on data confidentiality, industrial audits prioritize availability, physical process safety, and the deterministic integrity of real-time control loops. With global industrial cyber attacks rising significantly and critical infrastructure regulations hardening worldwide, achieving formal IEC 62443 certification is an essential operational baseline.
Navigating the multi-tiered structure of the standard demands rigorous preparation across risk assessment, zone architecture, and technical security levels. Below are the top 12 expert steps to successfully prepare your industrial enterprise for an IEC 62443 audit.
Best 12 Steps to Prepare for an IEC 62443 Audit
1. Define the System Under Consideration (SuC) and Scope Boundaries
Before an auditor examines a single configuration file or firewall rule, you must precisely define the boundaries of your System under Consideration. In complex industrial plants, attempting to audit the entire enterprise network simultaneously leads to failure. Clearly demarcate physical process units, SCADA control networks, and associated safety instrumented systems so auditors can evaluate specific asset collections without structural ambiguity or overlap.
2. Conduct a Comprehensive Industrial Cyber Security Risk Assessment
IEC 62443-3-2 mandates thorough cybersecurity risk assessments tailored specifically to industrial operational processes. Identify all potential threat vectors, worst-case consequences of process disruption, and existing vulnerabilities across your plant floor. Auditors will look for documented risk matrices that tie technical vulnerabilities directly to operational and physical safety impacts, rather than generic IT risk scores.
3. Establish and Document Zones and Conduits Architecture
Network segmentation is a foundational pillar of IEC 62443 compliance. Divide your industrial environment into distinct security zones based on functional criticality and similarity, and govern data flow between them via defined conduits. Prepare detailed network topology diagrams showing how firewalls, data diodes, and industrial security gateways enforce boundary protection between enterprise IT and Level 2 or Level 3 control zones.
4. Implement Shieldworkz for Automated OT Posture Auditing
Maintaining continuous visibility across heterogeneous industrial assets, legacy programmable logic controllers (PLCs), and modern IIoT devices is critical for audit readiness. Shieldworkz OT Security & Forensic Platform delivers advanced, automated asset discovery, continuous posture monitoring, and deep protocol traffic parsing tailored for industrial environments. During audit preparation, Shieldworkz provides real-time validation of network topologies, tracks configuration drift, and generates comprehensive compliance reports to prove continuous adherence to IEC 62443 security levels without interrupting plant availability.
5. Validate Target Security Levels (SL-T) Versus Achieved Levels (SL-A)
IEC 62443 utilizes Security Levels (SL 1 through SL 4) to quantify required and achieved defense postures. Auditors will verify whether your Security Level Target, defined during initial risk assessments, matches your Security Level Achieved. Review your technical control implementations across identification, authentication, and system integrity to ensure field devices and controllers meet or exceed mandated capability thresholds.
6. Audit Identity and Access Management (IAM) for OT Operators
Enterprise IT IAM policies rarely translate cleanly to plant floors where shared engineering accounts and legacy operator login credentials often persist. Standardize multi-factor authentication, implement Privileged Access Management for third-party vendor maintenance portals, and establish rigorous role-based access control to prove absolute adherence to strict user authentication mandates.
7. Gather Hardware and Firmware Inventories (SBOM + HBOM)
Auditors require complete transparency into what is running inside your industrial devices. Compile detailed Software Bills of Materials and Hardware Bills of Materials covering embedded operating systems, microcontrollers, FPGA firmware, and third-party communication libraries. Demonstrating a structured mechanism for tracking component vulnerabilities and firmware lifecycles is essential for satisfying standard requirements.
8. Review and Hardening of Legacy Industrial Protocols
Many legacy industrial protocols, such as Modbus, DNP3, and OPC Classic, lack native encryption and authentication. Auditors will scrutinize how you protect these unencrypted protocols. Document compensating controls such as industrial deep packet inspection firewalls, encrypted tunneling, and localized network micro-segmentation deployed to shield vulnerable legacy controllers from internal tampering.
9. Establish Robust Patch Management and VEX Workflows
Applying unvetted patches to live industrial machinery can cause catastrophic downtime. Auditors expect a mature patch management workflow backed by Vulnerability Exploitability eXchange documents. Demonstrate how your engineering teams evaluate vendor patches in a staging environment, assess true exploitability in your specific architecture, and coordinate updates with plant safety committees.
10. Test and Document Incident Response and Recovery Playbooks
An IEC 62443 audit evaluates your organization’s resilience when containment is required. Review and update your cyber-physical incident response playbooks to ensure they account for physical safety interlocks, manual overrides, and safe-state plant operations. Provide documentation of recent tabletop exercises and cross-functional drills involving both IT security analysts and plant safety engineers.
11. Verify Configuration Management and Change Control Logs
Unauthorized logic changes to PLCs or safety controllers represent severe compliance violations. Implement automated file integrity monitoring and configuration tracking tools across all engineering workstations and controllers. Present auditors with immutable audit trails showing that every ladder logic modification or firmware update followed a strict, authorized change management approval workflow.
12. Conduct a Mock Audit and Gap Remediation Cycle
Before the official certification body arrives, execute a rigorous internal mock audit simulating the exact evaluation framework of IEC 62443-2-4 or 3-3. Use this dry run to identify documentation gaps, unmapped zones, or lingering configuration drift. Remediate these findings proactively to ensure a smooth, first-pass success during the formal audit.
Conclusion
Preparing for an IEC 62443 audit is much more than a box-ticking exercise for regulatory compliance-it is a vital operational strategy to safeguard industrial control systems against sophisticated cyber threats. By systematically scoping your systems, enforcing robust network segmentation, deploying advanced OT security platforms like Shieldworkz, and aligning technical controls with rigorous maturity models, industrial organizations can successfully navigate the audit process. Embracing these 12 steps ensures long-term operational resilience, protects human lives, and secures critical infrastructure for the future.