
Best 10 Ways to Run Safe OT Pen Tests Without Disrupting Production
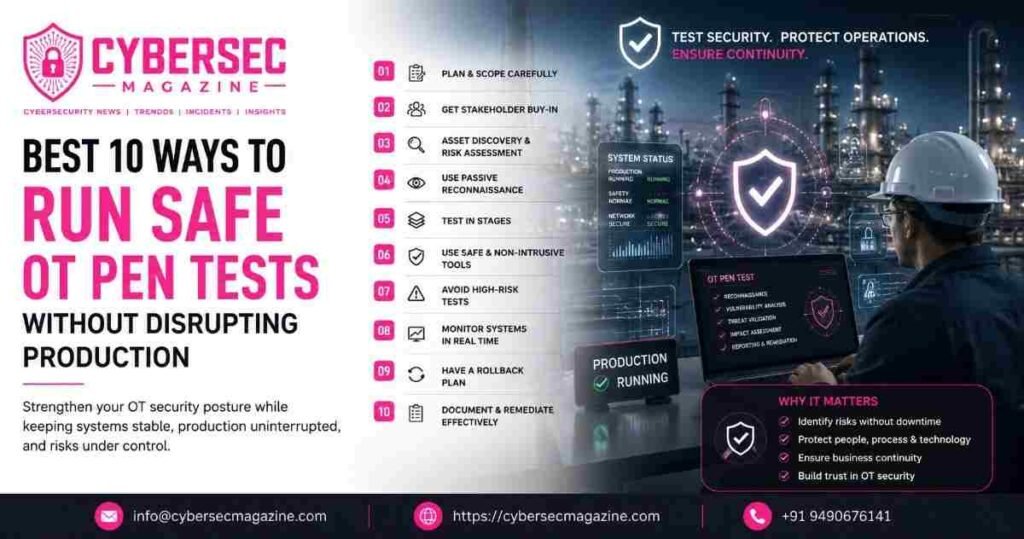
Operational Technology (OT) and Industrial Control Systems (ICS) form the backbone of modern critical infrastructure. Unlike traditional IT environments-where a failed security scan or an interrupted server process results in temporary data latency-a crash on a live Programmable Logic Controller (PLC), Human-Machine Interface (HMI), or Distributed Control System (DCS) can trigger catastrophic real-world consequences. Unplanned shutdowns in high-yield manufacturing, power grids, oil refineries, and water treatment facilities can cost millions of dollars per hour, damage expensive physical machinery, and pose severe human safety hazards.
Because legacy industrial protocols (e.g., Modbus/TCP, EtherNet/IP, DNP3, PROFINET) often lack basic network stack protections and rate-limiting, standard IT penetration testing tactics like aggressive port scanning, automated fuzzing, and intrusive exploit execution are extremely dangerous to deploy on live production networks. However, security teams must still validate their security posture against modern cyber-physical threats, enforce IEC 62443 standards, and satisfy regulatory mandates like NIST SP 800-82.
Achieving maximum security visibility without causing operational downtime requires a specialized, safety-first methodology. Based on field-tested OT red-teaming practices and industrial threat intelligence.
Best 10 Ways to Run Safe OT Pen Tests Without Disrupting Production
1. Establish Strict Rules of Engagement (RoE) and Plant-Operator Safeguards
Conducting a safe OT penetration test begins long before transmitting a single network packet, requiring deep operational alignment between red team testers and plant floor engineers. The Rules of Engagement (RoE) must clearly define explicitly out-of-bounds target assets-such as active safety instrumented systems (SIS), critical protection relays, and live chemical feed PLCs-while establishing hard boundaries on allowed testing windows. Crucially, an experienced OT operator or Control System Engineer must stand by with real-time access to process controls during every active testing phase, armed with an immediate “abort button” protocol to halt all testing instantly if any physical process anomaly, communication latency spike, or trip warning occurs.
2. Shift to Passive Reconnaissance and SPAN/TAP Network Analysis
Traditional IT pen tests rely heavily on active network sweeps to discover open ports and live hosts, but active probes can cause fragile embedded OT microcontrollers to freeze or reboot. Security teams should replace active scanning in live production zones with passive network monitoring, tapping switch SPAN/Mirror ports to record ambient industrial traffic without introducing a single packet onto the wire. By parsing captured PCAP files through protocol-aware inspection tools, testers can map complete network topologies, identify vulnerable firmware versions, and uncover unencrypted communication channels without risking device stability or control loop latency.
3. Leverage High-Fidelity Digital Twins and Staging Testbeds for Destructive Exploitation
To safely evaluate high-risk exploits, zero-day vulnerabilities, or heavy protocol fuzzing without risking live manufacturing runs, security analysts must decouple exploitation from production floor hardware. Establishing offline digital twins, virtualized SCADA environments, or hardware-in-the-loop (HIL) lab testbeds allows red teams to execute intrusive payloads against exact replicas of production PLCs, HMIs, and engineering workstations. Testing in a controlled lab environment provides definitive proof of exploitability and physical impact while completely insulating operational processes from downtime.
4. Conduct Controlled IT-to-OT Pivot Testing at Purdue Level 3.5
The vast majority of cyberattacks targeting industrial facilities originate within enterprise IT networks and attempt to move laterally into production zones across the Industrial DMZ (iDMZ). Rather than executing risky attacks directly on Purdue Level 1 field devices, testers should focus active penetration efforts on validating the strength of Purdue Level 3.5 conduits and remote access controls. Controlled pivoting tests evaluate whether compromised corporate domain credentials, misconfigured jump hosts, or unauthorized VPN tunnels permit entry into SCADA supervisory zones (Level 2/3), highlighting critical path weaknesses before attackers reach physical control loops.
5. Implement OT-Aware Slow and Paced Scanning Techniques
When active network probing is strictly required to verify device responsiveness or confirm firewall rulesets, standard high-speed automated scanners like Nmap must never be used with default IT timing templates. OT network stacks and low-powered serial-to-Ethernet converters easily suffer buffer exhaustion when flooded with rapid TCP handshake requests, leading to dropped connection states on critical equipment. Penetration testers must configure custom, low-rate packet transmissions-using dedicated OT-aware scripts that pace requests, throttle connection counts, and strictly avoid intrusive OS finger-printing payloads-to safely validate network exposure.
6. Conduct Comprehensive Offline Configuration and Logic File Audits
Significant OT security risk stems from poor system configurations, hardcoded vendor passwords, unencrypted protocol settings, and unvalidated PLC ladder logic. Testers can uncover these critical vulnerabilities entirely offline without sending network traffic into live production lines. By performing static analysis on exported PLC project files, HMI backup configurations, router/firewall rulesets, and Engineering Workstation (EWS) software builds, red teams can identify systemic authorization flaws, unpatched software dependencies, and hardcoded backdoor credentials with absolute production safety.
7. Audit Physical Security and Removable Media Entry Points
Industrial environments often feature strong perimeter network defenses but remain highly vulnerable to physical intrusion and unvetted removable media. Security assessments must evaluate physical security controls across plant gates, sub-fab utility rooms, server enclosures, and unmonitored USB ports on operator HMI terminals. Testing whether an analyst can physically attach a rogue wireless drop-box to an open switch port or insert an unvetted USB payload into an air-gapped terminal tests real-world attack vectors without disrupting active industrial control processes.
8. Perform Protocol-Aware Message Validation Instead of Arbitrary Fuzzing
Fuzzing industrial communications by sending malformed or random data streams to field controllers frequently crashes legacy OT network stacks, requiring a hard physical reset of the device. Instead of arbitrary payload generation, testers should use protocol-aware assessment techniques that strictly conform to standard industrial specifications (such as Modbus/TCP or EtherNet/IP CIP structures). By issuing valid but unauthorized function calls (such as read/write requests to unlinked register addresses) in a controlled manner, analysts can verify whether endpoints enforce proper authorization without destabilizing the host system.
9. Execute Assessments Exclusively During Scheduled Maintenance Windows
If active testing on production-connected networks, supervisory HMIs, or Level 2 control servers is unavoidable, assessments must be scheduled strictly during planned plant turnarounds or maintenance outages. Conducting active tests while the physical process is offline or idling ensures that even if an unexpected device lockup occurs, no live silicon wafers, chemical batches, or power transmission cycles are ruined. Furthermore, maintenance windows allow plant engineering teams to quickly reboot or re-flash affected controllers without impacting operational availability metrics.
10. Implement Continuous Telemetry Monitoring and Real-Time Latency Checks
During any active testing phase, security teams must continuously monitor the operational health and performance metrics of the underlying OT network. Deploying continuous network performance tools to track round-trip latency, packet loss, PLC CPU utilization, and SCADA alarm logs provides immediate feedback on system stress. If latency increases beyond pre-established baseline thresholds or if anomalous process alarms trigger on control room consoles, testing must instantly pause to evaluate system stability before proceeding.
Conclusion
Conducting penetration testing in Operational Technology environments is no longer optional-it is a vital requirement for identifying hidden attack paths and maintaining cyber resilience against sophisticated threat actors. However, applying aggressive IT security testing methods to live industrial networks introduces unacceptable operational risk. By adopting a safety-first approach-grounded in passive monitoring, offline configuration analysis, lab-based digital twins, and strict operator-guided rules of engagement-organizations can rigorously validate their OT defenses without risking physical safety or production continuity.