
Best 10 Ways to Protect Machine-to-Machine (M2M) Credentials
Welcome back to the cybersecurity desk. As an editor mapping the high-stakes convergence of IT, OT, and MIoT, I spend a lot of time analyzing how humans authenticate. But in 2026, humans aren’t the primary users on our networks-machines are.
As we scale microservices, deploy millions of Industrial IoT (IIoT) sensors, and connect legacy PLCs to cloud analytics platforms, Machine-to-Machine (M2M) communication has become the central nervous system of modern operations. However, this massive web of automated API calls and backend synchronization tasks introduces a severe vulnerability: M2M credentials.
Unlike human users who can respond to MFA prompts or biometric scans, machines rely on static secrets, client IDs, and tokens. If an adversary compromises an M2M credential, they gain an automated, unblinking backdoor into your most critical data and control loops. Securing these non-human identities requires a radically different approach than traditional Identity and Access Management (IAM).
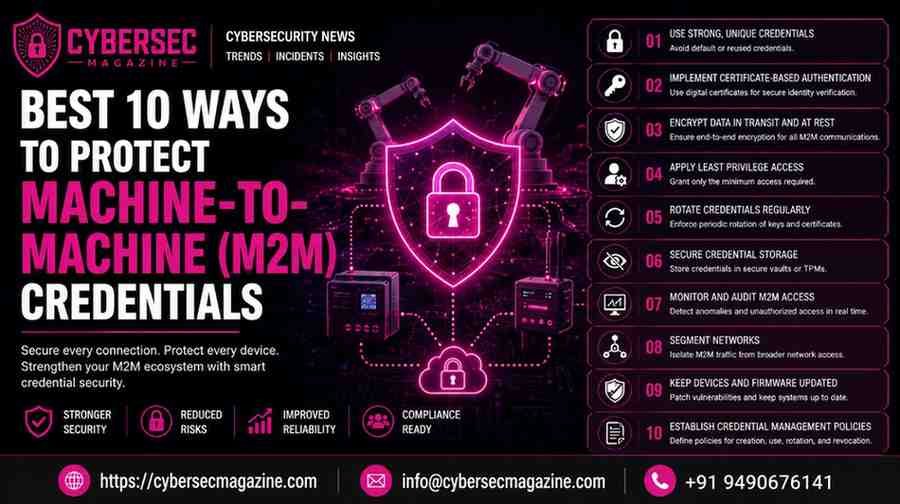
Best 10 Ways to Protect Machine-to-Machine (M2M) Credentials
1. Never Hardcode Secrets in Source Code
This is the cardinal sin of M2M security, yet it remains astonishingly common. Developers must never embed client_id or client_secret values directly into application source code or commit them to version control repositories like Git. Hardcoded secrets are easily discoverable by threat actors who scan public and private repositories. Instead, inject credentials securely at runtime using environment variables or configuration managers.
2. Mandate the Use of Secure Secret Vaults
Client credentials must be treated like the crown jewels. Store them in dedicated, encrypted secure vaults such as AWS Secrets Manager, HashiCorp Vault, or Azure Key Vault. These tools ensure that secrets are encrypted at rest and protected by strict access controls. Crucially, only store the client credentials in the vault; never persist the actual access tokens, which should only be cached in memory temporarily.
3. Enforce Short-Lived Access Tokens (TTL)
When a machine authenticates via OAuth 2.0 Client Credentials Grant, it receives an access token. If this token is intercepted, the attacker has free reign until the token expires. You must configure extremely short Time-to-Live (TTL) expiration windows-ideally 5 to 15 minutes for most M2M use cases. Long-lived or infinite access tokens create an unacceptable window of opportunity for lateral movement.
4. Implement Mutually Authenticated TLS (mTLS)
For high-security internal microservices, move away from shared secrets and tokens entirely. Mutually Authenticated TLS (mTLS) requires both the client and the server to verify each other’s cryptographic certificates before a connection is established. This means services trust only specific certificates, allowing for granular, identity-based access control that prevents unauthorized machines from even initiating a handshake.
5. Transition to Asymmetric Client Authentication
Where mTLS isn’t feasible (such as certain external API integrations), upgrade from symmetric shared secrets to asymmetric authentication methods like Private Key JWT. In this model, the client signs a JSON Web Token (JWT) with its private key to authenticate, meaning no sensitive secret is ever transmitted over the network. This provides a much higher layer of cryptographic assurance and improves auditability.
6. Automate Credential Rotation
Static credentials degrade in security value over time. You must automate the rotation of client secrets on a strict, regular schedule (e.g., every 30 to 90 days). Modern M2M architectures should facilitate zero-downtime rotations where a new credential is generated, the old one is deprecated, and vaults are updated seamlessly via API integrations without requiring human intervention.
7. Strictly Limit Token Scopes (Least Privilege)
A machine should only have access to the exact resources required to perform its specific task. When configuring M2M authorization, avoid wide or “catch-all” scopes. If a billing microservice only needs to read customer data, its token scope must strictly prohibit write or delete access. Limiting the scope minimizes the “blast radius” if the machine’s credentials are ever compromised.
8. Enforce Rate Limiting on Token Endpoints
Your OAuth provider’s token generation endpoint is a prime target for credential stuffing and Denial of Service (DoS) attacks. You must enforce strict rate limits on how frequently a specific client ID or IP address can request new tokens. This prevents adversaries from overwhelming the authorization server or attempting to brute-force authentication mechanisms.
9. Always Encrypt Transport with HTTPS
This should be fundamental, but it warrants repeating for legacy OT environments transitioning to IP networks. All M2M token exchanges, API requests, and secret retrievals must occur over encrypted HTTPS channels. Transmitting tokens or client secrets in plaintext allows network sniffers to easily harvest credentials in transit, completely undermining your authentication framework.
10. Audit and Monitor Token Usage Continuously
Even the best preventative controls can fail. You must actively monitor and log all M2M authentication events, token issuances, and API usage patterns. Integrate these logs with your SIEM to detect anomalies-such as a token being used outside of its expected geographic location, an unusual spike in API calls, or requests occurring during off-hours. Early anomaly detection is your safety net for compromised credentials.
Conclusion
The industrial and corporate networks of 2026 run on automation, and automation requires secure machine identity. Treating M2M credentials with the same (or greater) rigor as human passwords is no longer optional. By moving away from static, hardcoded secrets toward dynamic, short-lived tokens, cryptographic certificates, and continuous monitoring, organizations can lock down their automated infrastructure and stop threat actors from turning their own machines against them.