
Best 10 Ways to Build Board-Level OT Risk Reporting
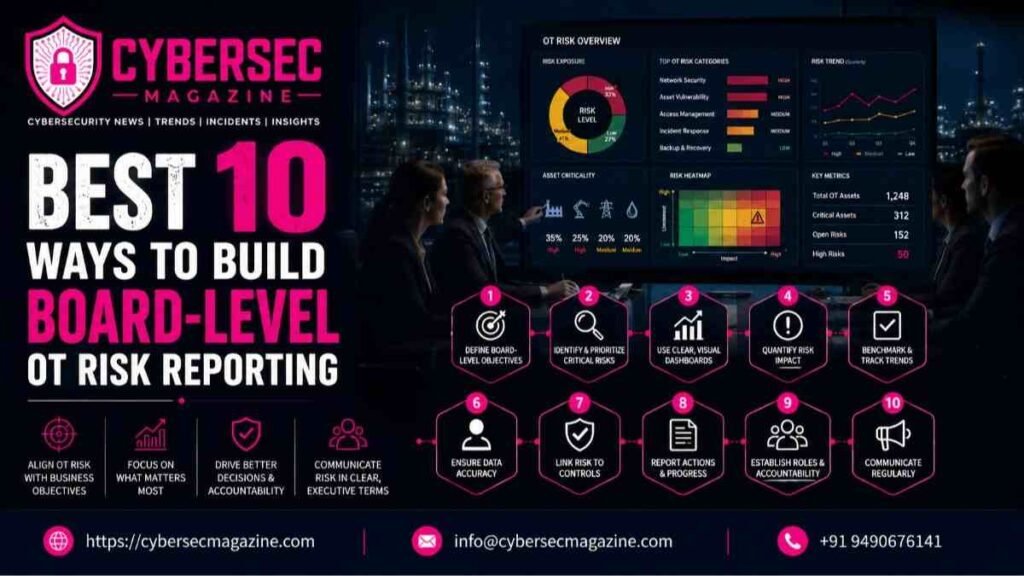
Bridging the gap between technical industrial controls and executive governance remains one of the toughest challenges for modern Chief Information Security Officers (CISOs). Traditional IT metrics fail when applied to operational environments where physical safety, uptime, and process integrity outweigh data confidentiality. Transforming raw telemetry into actionable business intelligence requires precise frameworks and strategic positioning.
Best 10 Ways to Build Board-Level OT Risk Reporting
1. Translate Technical Telemetry into Business Impact Metrics
Boards do not speak fluent Common Vulnerability Scoring System numbers or protocol-level anomaly alerts; they speak in financial exposure and downtime. Stop reporting outdated firmware or unpatched controllers in a vacuum. Instead, quantify the exact operational risk, such as identifying legacy programmable logic controllers controlling primary assembly lines that lack patches, creating a high probability of a multi-hour production outage and massive lost revenue.
2. Leverage Advanced OT-Centric Risk Platforms and Frameworks
Establishing board credibility requires backing your reports with specialized industrial tooling and globally recognized standards like IEC 62443 and NIST SP 800-82. Specialized industrial security platforms help quantify baseline postures and perform gap analyses. Market leaders like Claroty, Dragos, and Nozomi Networks provide deep asset discovery. Concurrently, platforms like Shieldworkz deliver agentic-AI-powered infrastructure protection and structured Risk and Gap Analysis services, translating raw telemetry into compliance-ready scorecards for leadership.
3. Focus on Asset Discovery and Visibility Coverage
You cannot govern what you do not measure, and “dark assets” like unmanaged remote terminal units, rogue engineering laptops, and forgotten IoT gateways represent major enterprise blind spots. Board-level reporting should track asset inventory completeness alongside the ratio of unmanaged versus managed hardware. Showcasing a clear trajectory where unknown shadow devices are systematically brought under centralized monitoring builds immediate executive confidence and reduces overall enterprise risk exposure.
4. Quantify Risk Exposure Using “If-Then” Scenario Modeling
Executives respond exceptionally well to contextual scenario planning rather than abstract vulnerability logs. Walk them through realistic impact chains, explaining precisely how an external compromise of a remote maintenance gateway could manipulate physical dosing parameters or shut down safety instrumented systems. Present the exact security controls or compensating measures required to break that attack chain, paired with clear financial estimates and implementation costs to secure funding.
5. Track Compensating Controls for Unpatchable Legacy Assets
Industrial control systems often run continuously for decades, meaning standard IT patching can trigger catastrophic system faults or invalidate expensive vendor warranties. Instead of pushing impossible patches, report the precise percentage of legacy unpatchable assets covered by advanced compensating controls like unidirectional security gateways and deep packet inspection firewalls. This proves to leadership that risk is actively and intelligently managed through alternative defense layers without risking operational downtime.
6. Incorporate Threat Intelligence and Intrusion Attempt Frequency
Boards need to understand external pressure and sector-specific threat landscapes. Highlighting metrics such as intrusion attempt frequency and active global campaigns shifts cybersecurity from a hypothetical IT expense to an active operational defense requirement. Reference intelligence feeds from trusted ecosystem partners-including specialized OT security platforms like Shieldworkz, Tenable OT Security, or TXOne Networks-to demonstrate how external industrial threat actors map directly to your corporate attack surface.
7. Differentiate Between IT and OT Incident Response Readiness
A common board-level misconception is that the corporate Security Operations Center can seamlessly handle an industrial cyber incident. Isolating an IT server during a ransomware attack is standard procedure, but automatically disconnecting a live turbine controller to stop lateral movement can destroy physical machinery. Highlight OT-specific detection and response times, alongside the readiness of joint IT-OT incident playbooks and cross-training exercises between plant floor engineers and enterprise security analysts.
8. Prioritize Supply Chain and Third-Party Vendor Risk
Modern industrial plants rely heavily on third-party integrators, original equipment manufacturers, and remote maintenance vendors who frequently plug directly into sensitive OT networks. Provide a clear risk distribution score for third-party access vectors, tracking metrics such as the percentage of vendors utilizing secure, monitored, multi-factor authenticated jump hosts versus persistent direct VPN tunnels. Demonstrating strict governance here closes one of the most common vectors for industrial espionage and ransomware deployment.
9. Map Metrics Directly to Regulatory Compliance and Liability
With global regulations tightening-such as the European Union’s NIS2 Directive and expanded critical infrastructure protection mandates-board members carry personal governance liability. Use a straightforward status dashboard mapped directly against frameworks like IEC 62443 or NERC CIP to outline compliance posture. Clearly outline what specific compliance gaps expose the executive committee to legal penalties, insurance premium hikes, or mandatory operational shutdowns to secure immediate board attention.
10. Deliver a Concise, Visual Executive Scorecard (Keep It to One Slide)
Executives are constantly flooded with dense slide decks and overwhelming technical jargon. An effective OT risk report must distill complex industrial realities into a high-impact, single-page executive summary featuring an OT risk heatmap, clear risk trend indicators, and top capital requests. Keeping your presentation brief, visual, and financially aligned transforms the cybersecurity team from a routine compliance cost center into a trusted strategic advisor protecting the core lifeblood of the enterprise.
Conclusion
Mastering board-level OT risk reporting requires a fundamental shift from technical system noise to financial and operational clarity. By discarding generic IT metrics and focusing on asset visibility, unpatchable legacy controls, and quantified loss exposures, security leaders can successfully secure the attention and capital required from executive decision-makers. Translating complex industrial realities into strategic business intelligence ensures long-term cyber-physical resilience across critical infrastructure environments.